AWS Certified SysOps Administrator – Associate (SOA-C01) Exam Learning Path

AWS Certified SysOps Administrator – Associate (SOA-C01) Exam Learning Path

⚠️ EXAM RETIRED – SOA-C01 No Longer Available

The AWS Certified SysOps Administrator – Associate (SOA-C01) exam has been retired. It was replaced by the SOA-C02 exam, which itself was retired on September 29, 2025.

The current exam is now the AWS Certified CloudOps Engineer – Associate (SOA-C03), launched on September 30, 2025.

Recommended Next Steps:

This content is maintained for historical reference only. If you are preparing for certification, please use the SOA-C03 exam resources.

AWS Certified SysOps Administrator – Associate (SOA-C01) exam was the AWS associate-level operations exam that validated the ability to:

  • Deploy, manage, and operate scalable, highly available, and fault tolerant systems on AWS
  • Implement and control the flow of data to and from AWS
  • Select the appropriate AWS service based on compute, data, or security requirements
  • Identify appropriate use of AWS operational best practices
  • Estimate AWS usage costs and identify operational cost control mechanisms
  • Migrate on-premises workloads to AWS

Refer AWS Certified SysOps – Associate Exam Guide Sep 18
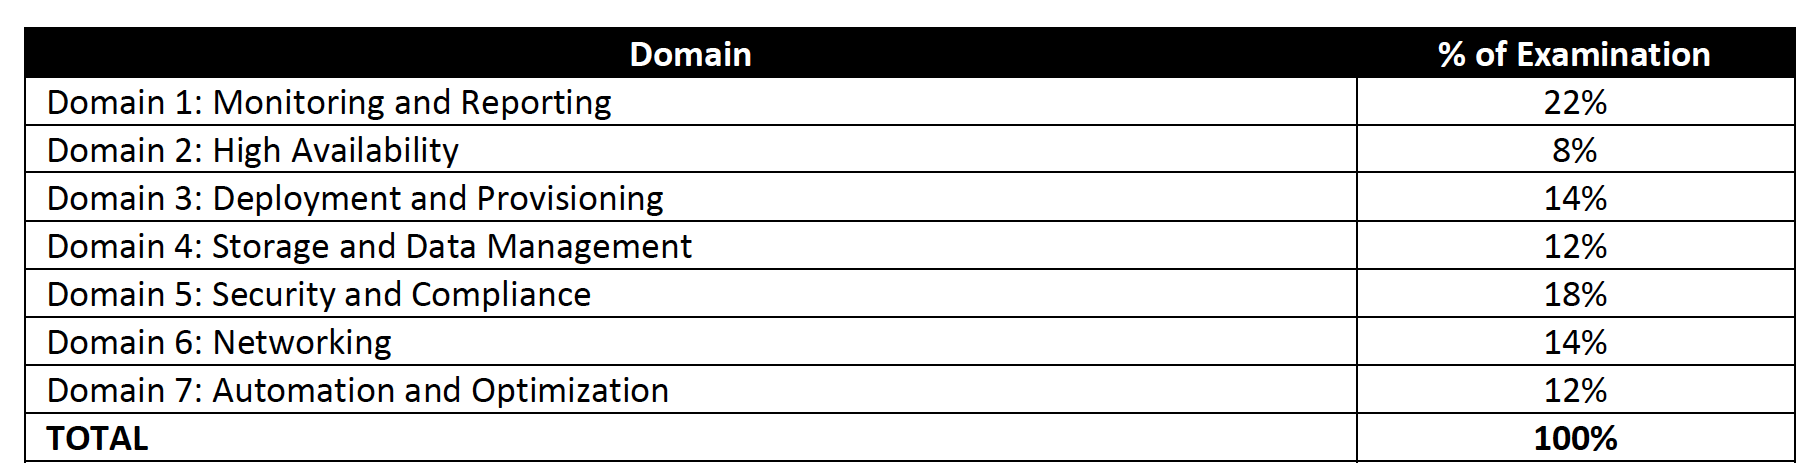
AWS Certified SysOps Administrator - Associate Content Outline

AWS Certified SysOps Administrator – Associate (SOA-C01) Exam Summary

  • AWS Certified SysOps Administrator – Associate exam was quite different from the previous one with more focus on the error handling, deployment, monitoring.
  • AWS Certified SysOps Administrator – Associate exam covered a lot of AWS services like ALB, Lambda, AWS Config, AWS Inspector, AWS Shield while focusing majorly on other services like CloudWatch, Metrics from various services, CloudTrail.
  • Be sure to cover the following topics
    • Monitoring & Management Tools
      • Understand CloudWatch monitoring to provide operational transparency
        • Know which EC2 metrics it can track (disk, network, CPU, status checks) and which would need custom metrics (memory, disk swap, disk storage etc.)
        • Know ELB monitoring
          • Classic Load Balancer metrics SurgeQueueLength and SpilloverCount
          • Reasons for 4XX and 5XX errors
      • Understand CloudTrail for audit and governance
      • Understand AWS Config and its use cases
      • Understand AWS Systems Manager and its various services like parameter store, patch manager
      • Understand AWS Trusted Advisor and what it provides
      • Very important to understand AWS CloudWatch vs AWS CloudTrail vs AWS Config
      • Very important to understand Trust Advisor vs Systems manager vs Inspector
      • Know Personal Health Dashboard & Service Health Dashboard
      • Deployment tools
        • Know AWS OpsWorks and its ability to support chef & puppet
        • Know Elastic Beanstalk and its advantages
        • Understand AWS CloudFormation
          • Know stacks, templates, nested stacks
          • Know how to wait for resources setup to be completed before proceeding esp. cfn-signal
          • Know how to retain resources (RDS, S3), prevent rollback in case of a failure
    • Networking & Content Delivery
      • Understand VPC in depth
        • Understand the difference between
          • Bastion host – allow access to instances in private subnet
          • NAT – route traffic from private subnets to internet
          • NAT instance vs NAT Gateway
          • Internet Gateway – Access to internet
          • Virtual Private Gateway – Connectivity between on-premises and VPC
          • Egress-Only Internet Gateway – relevant to IPv6 only to allow egress traffic from private subnet to internet, without allowing ingress traffic
        • Understand
        • Understand how VPC Peering works and limitations
        • Understand VPC Endpoints and supported services
        • Ability to debug networking issues like EC2 not accessible, EC2 instances not reachable, Instances in subnets not able to communicate with others or Internet.
      • Understand Route 53 and Routing Policies and their use cases
        • Focus on Weighted, Latency routing policies
      • Understand VPN and Direct Connect and their use cases
      • Understand CloudFront and use cases
      • Understand ELB, ALB and NLB and what features they provide like
        • ALB provides content and path routing
        • NLB provides ability to give static IPs to load balancer.
    • Compute
      • Understand EC2 in depth
        • Understand EC2 instance types
        • Understand EC2 purchase options esp. spot instances and improved reserved instances options.
        • Understand how IO Credits work and T2 burstable performance and T2 unlimited
        • Understand EC2 Metadata & Userdata. Whats the use of each? How to look up instance data after it is launched.
        • Understand EC2 Security.
          • How IAM Role work with EC2 instances
          • IAM Role can now be attached to stopped and runnings instances
        • Understand AMIs and remember they are regional and how can they be shared with others.
        • Troubleshoot issues with launching EC2 esp. RequestLimitExceeded, InstanceLimitExceeded etc.
        • Troubleshoot connectivity, lost ssh keys issues
      • Understand Auto Scaling
      • Understand Lambda and its use cases
      • Understand Lambda with API Gateway
    • Storage
    • Databases
    • Security
      • Understand IAM as a whole
      • Understand KMS for key management and envelope encryption
      • Understand CloudHSM and KMS vs CloudHSM esp. support for symmetric and asymmetric keys
      • Know AWS Inspector and its use cases
      • Know AWS GuardDuty as managed threat detection service. Will help eliminate as the option
      • Know AWS Shield esp. the Shield Advanced option and the features it provides
      • Know WAF as Web Traffic Firewall
      • Know AWS Artifact as on-demand access to compliance reports
    • Integration Tools
      • Understand SQS as message queuing service and SNS as pub/sub notification service
        • Focus on SQS as a decoupling service
        • Understand SQS FIFO, make sure you know the differences between standard and FIFO
      • Understand CloudWatch integration with SNS for notification
    • Cost management

AWS Certified SysOps Administrator – Associate (SOA-C01) Exam Resources

📌 Note: The resources below were relevant for the retired SOA-C01 exam. For current certification preparation, refer to:

AWS Cloud Computing Whitepapers

AWS Certified SysOps Administrator – Associate (SOA-C01) Exam Contents

Domain 1: Monitoring and Reporting

  1. Create and maintain metrics and alarms utilizing AWS monitoring services
  2. Recognize and differentiate performance and availability metrics
  3. Perform the steps necessary to remediate based on performance and availability metrics

Domain 2: High Availability

  1. Implement scalability and elasticity based on use case
  2. Recognize and differentiate highly available and resilient environments on AWS

Domain 3: Deployment and Provisioning

  1. Identify and execute steps required to provision cloud resources
  2. Identify and remediate deployment issues

Domain 4: Storage and Data Management

  1. Create and manage data retention
  2. Identify and implement data protection, encryption, and capacity planning needs

Domain 5: Security and Compliance

  1. Implement and manage security policies on AWS
  2. Implement access controls when using AWS
  3. Differentiate between the roles and responsibility within the shared responsibility model

Domain 6: Networking

  1. Apply AWS networking features
  2. Implement connectivity services of AWS
  3. Gather and interpret relevant information for network troubleshooting

Domain 7: Automation and Optimization

  1. Use AWS services and features to manage and assess resource utilization
  2. Employ cost-optimization strategies for efficient resource utilization
  3. Automate manual or repeatable process to minimize management overhead

Exam Evolution: SOA-C01 → SOA-C02 → SOA-C03 (CloudOps Engineer)

The AWS SysOps Administrator certification has gone through significant evolution:

  • SOA-C01 (2018-2021) – Original version covered in this post. Focused on traditional operations with 7 domains.
  • SOA-C02 (2021-2025) – Added hands-on exam labs, introduced automation focus, reduced to 6 domains. Retired September 29, 2025.
  • SOA-C03 / AWS Certified CloudOps Engineer – Associate (2025-present) – Current exam. Rebranded to reflect modern cloud operations. Added containers (ECS, EKS, ECR), multi-account architectures, and expanded automation coverage. 5 domains with new question types (ordering, matching, case studies).

SOA-C03 Exam Domains (Current)

Domain Weight
Monitoring, Logging, Analysis, Remediation & Performance Optimization 22%
Reliability and Business Continuity 22%
Deployment, Provisioning, and Automation 22%
Networking and Content Delivery 18%
Security and Compliance 16%

Key additions in SOA-C03 compared to SOA-C01:

  • Container Operations – Amazon ECS, EKS, ECR, Fargate
  • Multi-Account Architecture – AWS Organizations, Service Control Policies (SCPs), AWS Control Tower
  • Modern Automation – AWS CDK, EventBridge, expanded Systems Manager capabilities
  • Cost Optimization – Compute Optimizer, AWS Budgets actions, Savings Plans
  • Enhanced Security – Security Hub, AWS Backup, Secrets Manager rotation

For the current exam preparation, refer to the official AWS CloudOps Engineer certification page.
AWS Certified Developer – Associate DVA-C01 Exam Learning Path

AWS Certified Developer – Associate DVA-C01 Exam Learning Path

⚠️ EXAM RETIRED — DVA-C01 No Longer Available

The AWS Certified Developer – Associate DVA-C01 exam was retired on February 27, 2023.

It has been replaced by the DVA-C02 exam. This content is maintained for historical reference only.

👉 For the current exam, see: AWS Certified Developer – Associate DVA-C02 Exam Learning Path

Key DVA-C02 Changes vs DVA-C01:

  • Domain restructuring — 4 domains: Development with AWS Services (32%), Security (26%), Deployment (24%), Troubleshooting & Optimization (18%)
  • More hands-on focus — Emphasis on writing, testing, deploying, and debugging code
  • New services — Amazon Q Developer, EventBridge, Step Functions, AppSync, CDK
  • AI-assisted development — Amazon Q Developer added in December 2024 revision
  • Removed focus — Less emphasis on architecture design, more on CI/CD workflows

AWS Certified Developer – Associate DVA-C01 exam was the AWS exam version available from June 2018 to February 2023 and has been replaced by the DVA-C02 exam. It validated:

  • Demonstrate an understanding of core AWS services, uses, and basic AWS architecture best practices.
  • Demonstrate proficiency in developing, deploying, and debugging cloud-based applications using AWS.

Refer AWS Certified Developer – Associate (Released June 2018) Exam Blue Print

AWS Certified Developer - Associate June 2018 Domains

AWS Certified Developer – Associate DVA-C01 Summary

  • AWS Certified Developer – Associate DVA-C01 exam was quite different from the previous one with more focus on the hands-on development and deployment concepts rather than just the architectural concepts
  • AWS Certified Developer – Associate DVA-C01 exam covered a lot of AWS services like Lambda, X-Ray while focusing majorly on other services like DynamoDB, Elastic Beanstalk, S3, EC2
  • Note: DVA-C01 was retired on Feb 27, 2023. For current exam preparation, refer to the DVA-C02 Learning Path

AWS Developer – Associate Exam Resources (Updated for DVA-C02)

AWS Developer – Associate DVA-C01 Exam Topics

  • Be sure to cover the following topics
    • Compute
      • Understand what AWS services you can use to build a serverless architecture?
      • Make sure you know and understand Lambda and serverless architecture, its features and use cases.
      • Know Lambda limits for e.g. execution time, deployable zipped and unzipped package limit
      • Be sure to know how to deploy, package using Lambda.
      • Understand tracing of Lambda functions using X-Ray
      • Understand integration of Lambda with CloudWatch.
      • Understand how to handle multiple releases using Alias
      • Know AWS Step Functions to manage Lambda functions flow
      • Understand Lambda with API Gateway
      • Understand API Gateway stages, ability to cater to different environments for e.g. dev, test, prod
      • Understand EC2 as a whole
      • Understand EC2 Metadata & Userdata. Whats the use of each? How to look up instance data after it is launched.
      • Understand EC2 Security. How IAM Role work with EC2 instances.
      • Understand how does EC2 evaluates the order of credentials, when multiple are provided. Remember the order – Environment variables -> Java system properties -> Default credential profiles file -> ECS container credentials -> Instance Profile credentials
      • Know Elastic Beanstalk at a high level, what it provides and its ability to get an application running quickly
      • Understand Elastic Beanstalk configurations and deployment types with their advantages and disadvantages
    • Databases
      • Understand relational and NoSQLs data storage options which include RDS, DynamoDB and their use cases
      • Understand DynamoDB Secondary Indexes
      • Make sure you understand DynamoDB provisioned throughput for Read/Writes and its calculations
      • Make sure you understand DynamoDB Consistency Model – difference between Strongly Consistent and Eventual Consistency
      • Understand DynamoDB with its low latency performance, DAX
      • Know how to configure fine grained security for DynamoDB table, items, attributes
      • Understand DynamoDB Best Practices regarding
        • table design
        • provisioned throughput
        • Query vs Scan operations
        • improving Scan operation performance
      • Understand RDS features – Read Replicas for scalability, Multi-AZ for High Availability
      • Know ElastiCache use cases, mainly for caching performance
      • Understand ElastiCache Redis vs Memcached
    • Storage
      • Understand S3 storage option
      • Understand S3 Best Practices to improve performance for GET/PUT requests
      • Understand S3 features like different storage classes with lifecycle policies, static website hosting, versioning, Pre-Signed URLs for both upload and download, CORS
    • Security
      • Understand IAM as a whole
      • Focus on IAM role and its use case especially with EC2 instance
      • Know how to test and validate IAM policies
      • Understand IAM identity providers and federation and use cases
      • Understand how AWS Cognito works and what features it provides
      • Understand MFA and How would implement two factor authentication for your application
      • Understand KMS for key management and envelope encryption
      • Know what services support KMS
        • Remember SQS, Kinesis now provides SSE support
      • Focus on S3 with SSE, SSE-C, SSE-KMS. How they work and differ?
      • Know how can you enforce only buckets to only accept encrypted objects
      • Know various KMS encryption options encrypt, reencrypt, generateEncryptedDataKey etc
      • Know how KMS impacts the performance of the services
    • Management Tools
      • Understand CloudWatch monitoring to provide operational transparency
      • Know which EC2 metrics it can track.
      • Understand CloudWatch is extendable with custom metrics
      • Understand CloudTrail for Audit
    • Integration Tools
      • Understand SQS as message queuing service and SNS as pub/sub notification service
      • Understand SQS features like visibility, long poll vs short poll
      • Focus on SQS as a decoupling service
      • AWS has released SQS FIFO, make sure you know the differences between standard and FIFO
      • Know the different development and deployment tools like CodeCommit, CodeBuild, CodeDeploy, CodePipeline
    • Networking
      • Does not cover much on networking or designing of networks, but be sure you understand VPC, Subnets, Routes, Security Groups etc.

AWS Cloud Computing Whitepapers

AWS Certified Developer – Associate DVA-C01 Exam Contents

Note: These domains are specific to the retired DVA-C01 exam. The current DVA-C02 exam has different domain structure and weightings. See the DVA-C02 Learning Path for current exam domains.

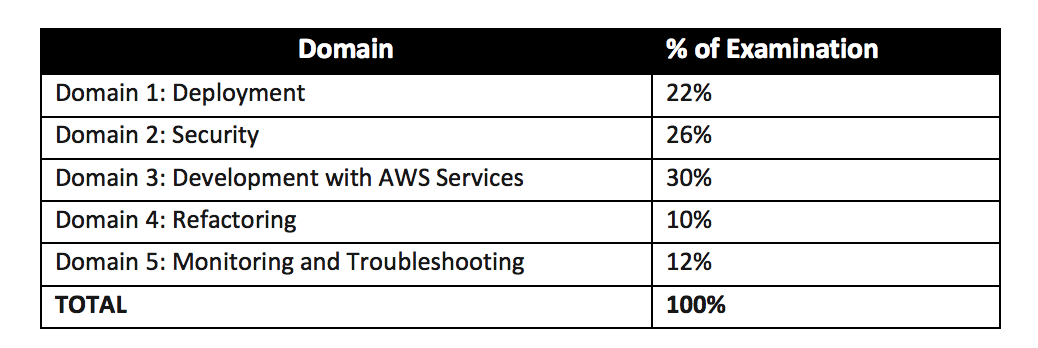
Domain 1: Deployment

  1. Deploy written code in AWS using existing CI/CD pipelines, processes, and patterns.
  1. Deploy applications using Elastic Beanstalk.
  1. Prepare the application deployment package to be deployed to AWS.
  2. Deploy serverless applications.

Domain 2: Security

  1. Make authenticated calls to AWS services.
  1. Implement encryption using AWS services.
  2. Implement application authentication and authorization.

Domain 3: Development with AWS Services

  1. Write code for serverless applications.
  1. Translate functional requirements into application design.
  1. Implement application design into application code.
  2. Write code that interacts with AWS services by using APIs, SDKs, and AWS CLI.

Domain 4: Refactoring

  1. Optimize application to best use AWS services and features.
  2. Migrate existing application code to run on AWS.

Domain 5: Monitoring and Troubleshooting

  1. Write code that can be monitored.
  2. Perform root cause analysis on faults found in testing or production.

DVA-C01 vs DVA-C02 — Key Differences

If you studied for DVA-C01 and need to understand what changed for DVA-C02:

  • Domain restructuring: DVA-C01 had 5 domains; DVA-C02 has 4 domains with different weightings
  • Refactoring domain removed: Merged into Development and Troubleshooting domains
  • More Lambda focus: Lambda gets its own dedicated task in DVA-C02
  • CI/CD emphasis: Greater focus on CodePipeline, CodeBuild, CodeDeploy, and CDK
  • New services added: EventBridge, AppSync, Step Functions, CDK, Amazon Q Developer
  • Services de-emphasized: Less focus on Elastic Beanstalk, more on containers (ECS/EKS)
  • Security weight increased: Security is now 26% of the exam (was 12% in DVA-C01)
  • AI-assisted development: December 2024 revision added Amazon Q Developer skills

For full DVA-C02 preparation guidance, visit the AWS Certified Developer – Associate DVA-C02 Exam Learning Path.

AWS Certified Solutions Architect – Associate SAA-C01 Exam Learning Path (Obsolete)

AWS Certified Solutions Architect – Associate SAA-C01 Exam Learning Path (Retired)

⚠️ EXAM RETIRED — SAA-C01 is No Longer Available

AWS Solutions Architect – Associate SAA-C01 was retired in 2020. It was succeeded by SAA-C02 (also retired August 29, 2022), and then by the current SAA-C03 exam.

This content is maintained for historical reference only. You cannot register for or take the SAA-C01 exam.

Current Exam:

What Changed (SAA-C01 → SAA-C03):

  • Greater focus on AWS Well-Architected Framework pillars
  • New services added: AWS Organizations, Control Tower, Lake Formation, EventBridge, Step Functions, EKS, Fargate, and more
  • Expanded security and governance coverage
  • More emphasis on hybrid cloud and migration strategies
  • Updated to reflect current AWS service landscape (2022+)

AWS Solutions Architect – Associate SAA-C01 Exam Summary (Historical)

AWS Solutions Architect – Associate SAA-C01 validated the ability to effectively demonstrate knowledge of how to architect and deploy secure and robust applications on AWS technologies:

  • Define a solution using architectural design principles based on customer requirements.
  • Provide implementation guidance based on best practices to the organization throughout the life cycle of the project.

The SAA-C01 exam focused on building scalable, highly available, cost-effective, performant, resilient, and operationally effective architectures across the following topic areas:

  • Be sure to cover the following topics
    • Networking
      • Be sure to create VPC from scratch. This is mandatory.
        • Create VPC and understand what’s a CIDR.
        • Create public and private subnets, configure proper routes, security groups, NACLs.
        • Create Bastion for communication with instances
        • Create NAT Gateway or Instances for instances in private subnets to interact with internet
        • Create two tier architecture with application in public and database in private subnets
        • Create three tier architecture with web servers in public, application and database servers in private.
        • Make sure to understand how the communication happens between Internet, Public subnets, Private subnets, NAT, Bastion etc.
      • Understand VPC endpoints and what services it can help interact
      • Understand difference between NAT Gateway and NAT Instance
      • Understand how NAT high availability can be achieved
      • Understand CloudFront as CDN and the static and dynamic caching it provides, what can be its origin (it can point to on-premises sources)
      • Understand Route 53 for routing, health checks and various routing policies it provides and their use cases mainly for high availability
      • Be sure to cover ELB in deep. AWS has introduced ALB and NLB and there are lot of questions on ALB
      • Understand ALB features with its ability for content based and URL based routing with support for dynamic port mapping with ECS
    • Storage
      • Understand various storage options S3, EBS, Instance store, EFS, Glacier and what are the use cases and anti patterns for each
      • Understand various EBS volume types and their use cases in terms of IOPS and throughput. SSD for IOPS and HDD for throughput
      • Understand Burst performance and I/O credits to handle occasional peaks
      • Understand S3 features like different storage classes with lifecycle policies, static website hosting, versioning, Pre-Signed URLs for both upload and download, CORS
      • Understand Glacier as an archival storage with various retrieval patterns
      • Understand Storage gateway and its different types
    • Compute
      • Understand EC2 as a whole
      • Understand Auto Scaling and ELB, how they work together to provide High Available and Scalable solution
      • Understand EC2 various purchase types – Reserved, On-demand and Spot and their use cases
      • Understand Lambda and serverless architecture, its features and use cases
      • Understand ECS with its ability to deploy containers and micro services architecture
      • Know Elastic Beanstalk at a high level, what it provides and its ability to get an application running quickly
    • Databases
    • Analytics
      • Understand Redshift as a data warehousing tool
      • Know Kinesis for real time data capture and analytics
    • Security
    • Management Tools
      • Understand CloudWatch monitoring to provide operational transparency
      • Know which EC2 metrics it can track. Remember, it cannot track memory and disk space/swap utilization
      • Understand CloudWatch is extendable with custom metrics
      • Understand CloudTrail for Audit
    • Integration Tools
      • Understand SQS as message queuing service and SNS as pub/sub notification service
      • Understand SQS features like visibility, long poll vs short poll
      • Focus on SQS as a decoupling service
      • Understand SQS FIFO and the differences between standard and FIFO

AWS Solutions Architect – Associate SAA-C01 Exam Resources (Archived)

Note: The resources below were relevant for the SAA-C01 exam (retired 2020). For current SAA-C03 study resources, visit the SAA-C03 Learning Path.

  • Online Courses (Historical)
  • General Preparation Tips (Still Valid)
    • Sign up with AWS for the Free Tier account which provides a lot of services to try for free
    • Read the FAQs for important topics, as they cover key points and are good for quick review

AWS Cloud Computing Whitepapers (Still Relevant)

AWS Solutions Architect – Associate SAA-C01 Exam Domains (Historical)

Domain 1: Design Resilient Architectures

  1. Choose reliable/resilient storage.
  2. Determine how to design decoupling mechanisms using AWS services.
  3. Determine how to design a multi-tier architecture solution.
  4. Determine how to design high availability and/or fault tolerant architectures.

Domain 2: Define Performant Architectures

  1. Choose performant storage and databases.
  2. Apply caching to improve performance.
  3. Design solutions for elasticity and scalability.

Domain 3: Specify Secure Applications and Architectures

  1. Determine how to secure application tiers.
  2. Determine how to secure data.
  3. Define the networking infrastructure for a single VPC application.

Domain 4: Design Cost-Optimized Architectures

  1. Determine how to design cost-optimized storage.
  2. Determine how to design cost-optimized compute.

Domain 5: Define Operationally-Excellent Architectures

  1. Choose design features in solutions that enable operational excellence.

Related Posts

Amazon EMR Best Practices

Best Practices for Using Amazon EMR

Amazon has made working with big data a lot easier. You can launch an EMR cluster in minutes for big data processing, machine learning, and real-time stream processing with the Apache Hadoop ecosystem. You can use the Management Console, the command line, or infrastructure-as-code tools like CloudFormation and Terraform to start several nodes with ease.

EMR pricing uses pay-per-second billing, which results in lower costs and you no longer have to worry about the hourly boundary.

EMR makes a whole bunch of the latest versions of open source software available to you. Currently, EMR supports over 20 open source projects including Apache Spark, Hive, HBase, Flink, Presto, Trino, Hudi, Iceberg, and Delta Lake, with new releases made every 4 to 6 weeks. This is very useful, especially for rapidly evolving open source projects such as Apache Spark where each release contains critical bug fixes and features. However, you are not forced to upgrade; a new release is made available if you choose to use it. Each EMR release now gets 24 months of standard support. With EMR, you can spin up a bunch of instances and process massive volumes of data residing on S3 at a reasonable cost.

EMR Deployment Options

Amazon EMR provides multiple deployment options to match your operational requirements:

  • EMR on EC2 – Traditional cluster-based deployment with full control over cluster configuration, including instance types and custom AMIs. Best for workloads requiring advanced configurations and persistent clusters.
  • EMR Serverless – Run applications without managing clusters. Resources automatically scale up and down based on your workload. Best for data analysts and engineers who want to focus on application logic without cluster management overhead.
  • EMR on EKS – Run EMR workloads on Amazon Elastic Kubernetes Service. Compute resources can be shared between Spark applications and other Kubernetes applications. Resources are allocated and removed on demand. Best for organizations already using Kubernetes for container orchestration.

Supported Applications and Frameworks

A variety of cluster management options are supported, including YARN. You can run the following:

  • HBase
  • Trino (formerly PrestoSQL – high-performance distributed SQL engine)
  • Presto (legacy; AWS recommends Trino going forward)
  • Spark (including Spark 4.0 with VARIANT data type, Spark Connect, and ANSI SQL compliance)
  • Apache Flink (stream processing)
  • Apache Hive
  • Tez
  • Apache Hudi, Apache Iceberg, Delta Lake (open table formats with ACID transactions)
  • Zeppelin
  • JupyterHub
  • Notebooks (EMR Studio Workspaces)
  • SQL editors

Apache Spark 4.0 on EMR (GA 2026)

Apache Spark 4.0 is now generally available on Amazon EMR across all deployment options (EMR Serverless, EMR on EC2, and EMR on EKS). Key features include:

  • VARIANT data type – Native semi-structured data handling for JSON without the need for complex parsing logic
  • Spark Connect – Bridges interactive development and production-scale execution, enabling thin client connectivity
  • ANSI SQL compliance – Build data pipelines using standard SQL without learning Spark-specific syntax
  • Enhanced streaming (transformWithState API) – Build stateful streaming applications with improved state management
  • Apache Iceberg v3 support – Default column values, deletion vectors, multi-argument transforms, and row lineage tracking
  • EMR Optimized Runtime – Runs Spark workloads up to 4.5× faster than open-source Apache Spark

AWS Connectors

Additionally, connectors to different AWS services are available; for example, you can use Spark to load Redshift (using the Redshift connector, which uses Redshift commands under the hood to get good throughput). You can access DynamoDB for analytics applications, use connectors for relational data, and integrate with Amazon S3 Tables and SageMaker Lakehouse.

AWS Glue

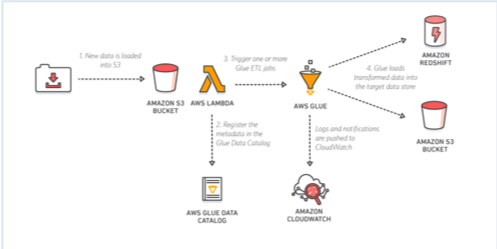
One particularly important integration is AWS Glue. AWS Glue (now at version 5.1) comprises several main components:

AWS Glue

  • AWS Glue ETL: Serverless ETL service supporting Apache Spark, with native fine-grained access control via AWS Lake Formation (table, column, row, and cell-level permissions). Glue 5.0+ adds support for SageMaker Lakehouse to unify data across S3 data lakes and Amazon Redshift data warehouses.
  • AWS Glue Data Catalog: A fully managed Hive metastore-compliant service. You have an intelligent metastore—you don’t have to write DDL to create a table; you can just make Glue crawl your data, infer what the schema is, and create those tables for you. It supports Apache Iceberg, Apache Hudi, and Delta Lake table formats, and automatically handles partition management. It also supports a variety of complex data types.
  • Crawlers: The crawlers crawl your data to infer the schema and automatically add partitions.
  • AWS Glue Data Quality: Provides rule-based data quality validation with rule labeling for organizing and analyzing data quality results.

AWS Glue is a managed service, so you spend less time monitoring. As a fully managed service, it is also responsible for infrastructure management and auto-scaling. Enabling security options in AWS Glue is straightforward, supporting IAM policies and AWS Lake Formation for fine-grained access control.

Open Table Formats

EMR now has first-class support for open table formats that enable ACID transactions, schema evolution, and time travel on data lakes:

  • Apache Iceberg – Supports v3 format with deletion vectors, materialized views, and merge-on-read. Recommended for most new data lake implementations.
  • Apache Hudi – Supports incremental data processing with upserts and deletes.
  • Delta Lake – Supports UniForm for cross-format compatibility with Iceberg clients.

All three formats are supported with AWS Lake Formation fine-grained access control (table, row, column, and cell-level filtering) across EMR on EC2, EMR Serverless, and EMR on EKS.

Common EMR Use Cases

EMR

HBase at massive scale: Using HBase with S3 for HFiles storage can save 50% or higher on storage costs compared to HDFS. Instead of sizing the cluster for HDFS, you size it for the processing power required for the HBase Region Servers. The S3 option also supports Read Replica HBase clusters in another AZ for load balancing and disaster recovery.

Real-time and batch processing: Use Amazon Kinesis Data Streams for pushing data to Spark. Use Spark Streaming or Apache Flink for real-time analytics or processing data on-the-fly and then dump that data into S3. If you don’t have real-time processing use cases, then Amazon Data Firehose (formerly Kinesis Data Firehose) is a great alternative. The data can be cataloged in the Glue Data Catalog and then accessed via a variety of analytical engines. EMR supports several analytical engines including Hive, Tez, Spark, and Trino. Once the data is in the Data Catalog on S3, you can use Athena (serverless SQL queries), Glue ETL (serverless ETL), and Redshift Spectrum.

Data exploration: Use Spark with EMR Studio (Jupyter-based notebooks), Zeppelin, or JupyterHub to arm data scientists with a way to explore large amounts of data. EMR Studio supports real-time collaboration and Git-based version control. Amazon SageMaker Unified Studio Notebooks also support EMR Serverless with Spark Connect for interactive analytics.

Ad hoc SQL queries: There is a big rise in the use of Trino (formerly PrestoSQL) for ad hoc SQL queries (in combination with Athena). Trino gives you advanced configurations and a way to build exactly what you need for your use case but requires cluster management, versus Athena where you just write SQL without infrastructure. Many BI tools support Trino for low latency dashboards. EMR 6.15+ runs Trino queries 2.7× faster than previous versions.

Deep learning with GPU instances: You can launch GPU hardware for EMR. TensorFlow is fully supported. Note that Apache MXNet has reached end-of-life and the project is archived—use PyTorch or TensorFlow instead for deep learning workloads on EMR.

Machine learning pipelines: Typical ML projects implement a multi-step process including ETL, feature engineering, model training, model evaluation, model deployment, and model scoring. Using Apache Spark for implementing ML pipelines is popular as it supports each step, scales for small and large jobs, has good ML libraries (MLlib), and has an active user base. Amazon SageMaker integrates with EMR for data preparation at scale.

EMR Deployment Best Practices

There are several options for deploying Spark on AWS:

  • EMR Serverless – No infrastructure to manage. Applications function as cluster templates that instantiate when jobs are submitted and can process multiple jobs. Automatic capacity management. Best for intermittent or variable workloads.
  • EMR on EC2 – Full control over instance types, cluster configurations, and custom AMIs. Supports batch and streaming, integrates with tooling. Best for persistent clusters with specific configuration requirements.
  • EMR on EKS – Run Spark on existing Kubernetes clusters. Share compute resources between Spark and other applications. Best for organizations standardized on Kubernetes.
  • EC2 (self-managed) – Maximum flexibility but places a huge management burden. Not recommended unless you have very specific requirements not met by managed options.

Lowering EMR Costs

If you are paying for Hadoop nodes that are not doing anything, then you are just burning money. Key cost optimization strategies:

  • Use EMR Serverless – Pay only for resources consumed during job execution. No idle cluster costs.
  • Use Graviton instances – AWS Graviton-based instances provide up to 40% better price-performance compared to equivalent x86 instances. EMR fully supports Graviton2 and Graviton3 instance types.
  • Use Spot Instances for task nodes – Achieve up to 60-90% cost savings on compute. Use Instance Fleets with diversified instance types across multiple Availability Zones for better Spot capacity.
  • Use Instance Fleets with allocation strategies – EMR supports prioritized and capacity-optimized-prioritized allocation strategies for better instance provisioning reliability and cost optimization.
  • Enable Managed Scaling – EMR evaluates cluster metrics every 5-10 seconds and makes optimized scaling decisions. Supports Advanced Scaling with configurable optimization index (cost vs. performance).
  • Batch workloads and shut down clusters – Take an inventory of jobs, batch them, and shut down clusters in-between. Use transient clusters for batch processing.
  • Separate clusters by workload – Instead of one large always-on cluster, use auto-scaling separate clusters optimized for each workload type.
  • Use Amazon Linux AMI with preinstalled customizations – Faster cluster creation with custom AMIs.
  • Use On-Demand Capacity Reservations (ODCRs) – For predictable, steady-state workloads to ensure capacity availability.
  • Right-size instances – Use AWS Compute Optimizer recommendations to match instance types to actual resource demands.

EMR Security Best Practices

  • Use v2 managed IAM policies – AWS is deprecating v1 managed policies (AmazonElasticMapReduceFullAccess). Migrate to the new v2 policies with least-privilege access.
  • Enable encryption – Use at-rest and in-transit encryption for data processed by EMR clusters.
  • Use Lake Formation – Apply fine-grained access control (table, row, column, cell-level) on open table formats across all EMR deployment options.
  • Use security groups – Restrict network access to EMR clusters and manage port access.

EMR Studio

Amazon EMR Studio is a managed IDE environment for developing, visualizing, and debugging applications written in R, Python, Scala, and PySpark using Jupyter notebooks. Key features:

  • Built-in real-time collaboration with peers
  • Git repository integration for version control
  • Workspaces that connect to EMR on EC2 clusters or EMR Serverless applications
  • Integration with SageMaker Unified Studio for AI/ML workflows
  • Support for Spark Connect (Spark 4.0) for interactive workloads

Amazon SageMaker Lakehouse Integration

Amazon SageMaker Lakehouse unifies all your data across Amazon S3 data lakes, Amazon S3 Tables, and Amazon Redshift data warehouses. With this integration:

  • Access and query unified data from EMR using Spark
  • Apply consistent governance through Lake Formation permissions
  • Capture data lineage of EMR Spark jobs into SageMaker Unified Studio
  • Use SageMaker Unified Studio for end-to-end analytics and AI/ML on a single platform

AWS Auto Scaling Lifecycle – Hooks & Warm Pools

Auto Scaling Lifecycle

  • Instances launched through the Auto Scaling group have a different lifecycle than that of other EC2 instances
  • Auto Scaling lifecycle starts when the Auto Scaling group launches an instance and puts it into service.
  • Auto Scaling lifecycle ends when the instance is terminated either by the user, or the Auto Scaling group takes it out of service and terminates it
  • AWS charges for the instances as soon as they are launched, including the time it is not in InService

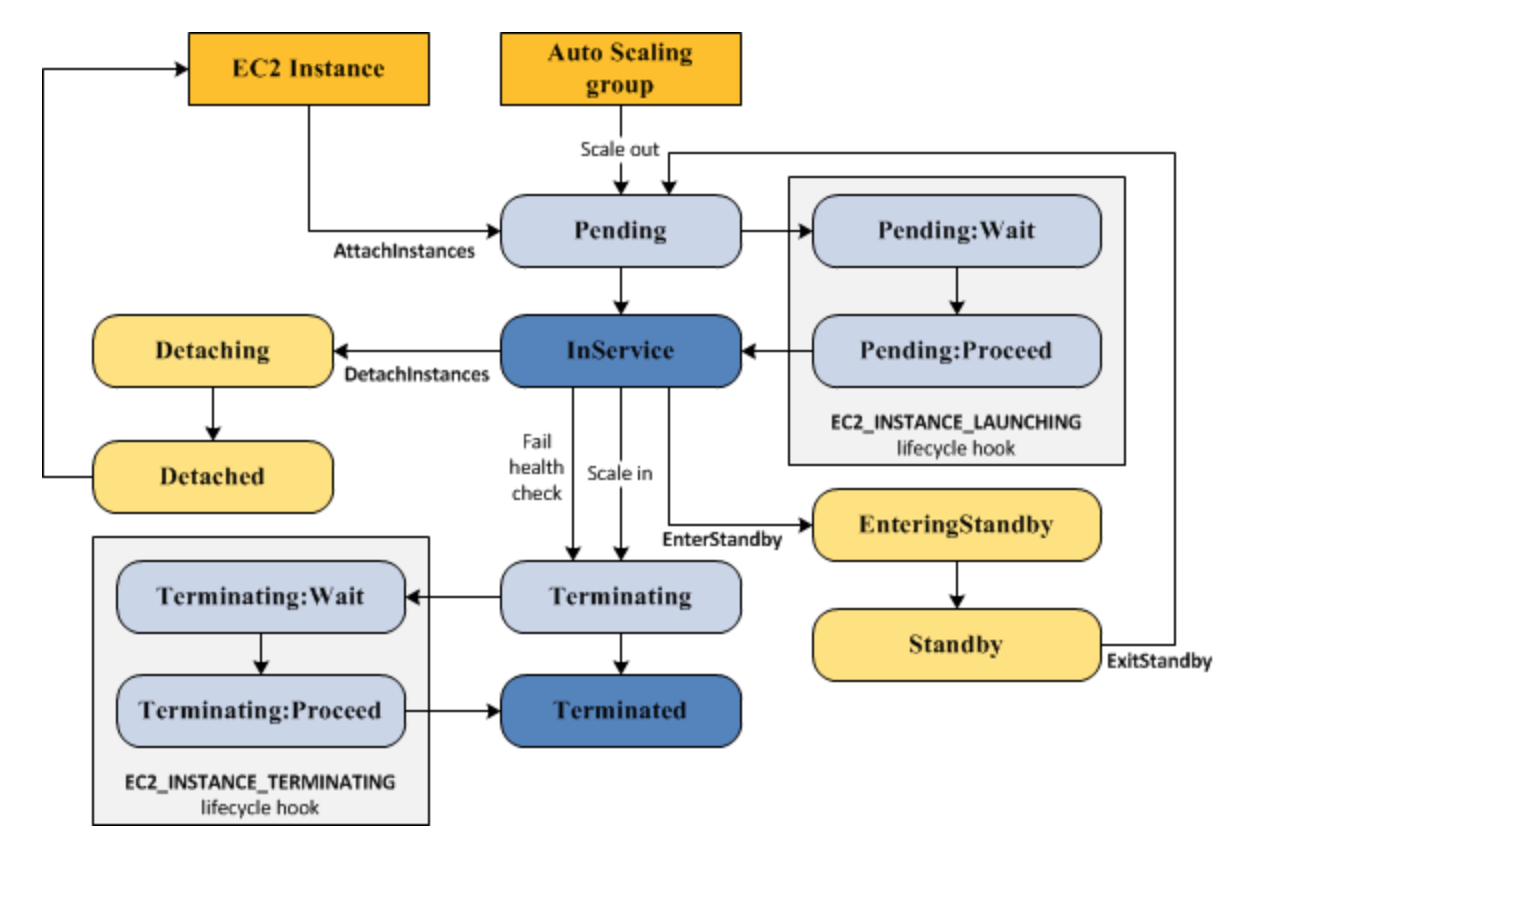
Auto Scaling Lifecycle Transition

Auto Scaling Group Lifecycle

Auto Scaling Lifecycle Hooks

  • Auto Scaling Lifecycle hooks enable performing custom actions by pausing instances as an Auto Scaling group launches or terminates them
  • Each Auto Scaling group can have multiple lifecycle hooks. However, there is a limit on the number of hooks per Auto Scaling group
  • Auto Scaling scale out event flow
    • Instances start in the Pending state
    • If an autoscaling:EC2_INSTANCE_LAUNCHING lifecycle hook is added, the state is moved to Pending:Wait
    • After the lifecycle action is completed, instances enter to Pending:Proceed
    • When the instances are fully configured, they are attached to the Auto Scaling group and moved to the InService state
  • Auto Scaling scale in event flow
    • Instances are detached from the Auto Scaling group and enter the Terminating state.
    • If an autoscaling:EC2_INSTANCE_TERMINATING lifecycle hook is added, the state is moved to Terminating:Wait
    • After the lifecycle action is completed, the instances enter the Terminating:Proceed state.
    • When the instances are fully terminated, they enter the Terminated state.
  • During the scale out and scale in events, instances are put into a wait state (Pending:Wait or Terminating:Wait) and are paused until either a continue action happens or the timeout period ends.
  • By default, the instance remains in a wait state for one hour, which can be extended by restarting the timeout period by recording a heartbeat.
  • If the task finishes before the timeout period ends, the lifecycle action can be marked completed and it continues the launch or termination process.
  • After the wait period, the Auto Scaling group continues the launch or terminate process (Pending:Proceed or Terminating:Proceed)
  • Custom actions can be implemented using the following notification targets:
    • Amazon EventBridge (Recommended) – Configure an EventBridge rule to invoke a Lambda function or other targets when an instance enters a wait state. EventBridge provides more options for which services you can target and makes it easier to handle events using serverless architecture.
    • AWS Lambda (Direct notification target) – Lambda functions can be specified directly as notification targets for lifecycle hooks, enabling custom actions when an instance enters a wait state without requiring EventBridge as an intermediary.
    • Amazon SNS – Publish notifications to an SNS topic that subscribers can receive and act on.
    • Amazon SQS – Send messages to an SQS queue (standard queues only; FIFO queues are not compatible with lifecycle hooks).
    • Create a script that runs on the instance as the instance starts. The script can control the lifecycle action using the ID of the instance on which it runs.

Auto Scaling Lifecycle Hooks Considerations

  • Keeping Instances in a Wait State
    • Instances remain in a wait state for a finite period of time.
    • Default is 1 hour (3600 seconds) with the max being 48 hours or 100 times the heartbeat timeout, whichever is smaller.
    • Time can be adjusted using
      • complete-lifecycle-action (CompleteLifecycleAction) command to continue to the next state if finishes before the timeout period end
      • put-lifecycle-hook command, the –heartbeat-timeout parameter to set the heartbeat timeout for the lifecycle hook during its creation
      • Restart the timeout period by recording a heartbeat, using the record-lifecycle-action-heartbeat (RecordLifecycleActionHeartbeat) command
  • Cooldowns and Custom Actions
    • Cooldown period helps ensure that the Auto Scaling group does not launch or terminate more instances than needed
    • Cooldown period starts when the instance enters the InService state. Any suspended scaling actions resume after cooldown period expires
  • Health Check Grace Period
    • Health check grace period does not start until the lifecycle hook completes and the instance enters the InService state
  • Lifecycle Action Result
    • Result of the lifecycle hook is either ABANDON or CONTINUE
    • If the instance is launching,
      • CONTINUE indicates a successful action, and the instance can be put into service.
      • ABANDON indicates the custom actions were unsuccessful, and that the instance can be terminated.
    • If the instance is terminating,
      • ABANDON and CONTINUE allow the instance to terminate.
      • However, ABANDON stops any remaining actions from other lifecycle hooks, while CONTINUE allows them to complete
  • Spot Instances
    • Lifecycle hooks can be used with Spot Instances. However, a lifecycle hook does not prevent an instance from terminating due to a change in the Spot Price, which can happen at any time

Instance Lifecycle Policy (Nov 2025)

  • Instance lifecycle policies allow configuring instance retention when termination lifecycle hooks fail or timeout, providing greater confidence in managing instances for graceful shutdown.
  • Instance lifecycle policies work in combination with termination lifecycle hooks, not as a replacement.
  • When configured, instances move to a Terminating:Retained state if the termination lifecycle action completes with an ABANDON result, instead of being terminated immediately.
  • Use instance lifecycle policies when:
    • Graceful shutdown is mandatory and failed shutdowns require manual intervention
    • Stateful applications must complete data persistence before termination
    • Applications require extended draining periods that may exceed the maximum lifecycle hook timeout of 48 hours
    • Workloads handling sensitive data where failed cleanup could result in data loss
  • How it works:
    • Termination lifecycle hooks are invoked and instance enters Terminating:Wait state
    • Graceful shutdown attempt begins
    • If the termination lifecycle action completes with ABANDON, the instance lifecycle policy evaluates and moves the instance to a retained state
    • Retained instances await manual action – they do NOT count toward the Auto Scaling group’s desired capacity
    • Auto Scaling launches replacement instances to maintain desired capacity
    • Standard EC2 charges apply for retained instances until manually terminated
    • Use TerminateInstanceInAutoScalingGroup API to terminate retained instances after completing necessary actions

Enter and Exit Standby

  • Instance in an InService state can be moved to Standby state.
  • Standby state enables you to remove the instance from service, troubleshoot or make changes to it, and then put it back into service.
  • Instances in a Standby state continue to be managed by the Auto Scaling group. However, they are not an active part of the application until they are put back into service.

Instance Refresh and Lifecycle Hooks

  • Instance refresh is used to update instances within an Auto Scaling group when configuration changes require instance replacement.
  • Lifecycle hooks execute during instance refresh operations (both launching new and terminating old instances).
  • Forced Cancellation (Sep 2025) – Instance refreshes can now be force-cancelled immediately without waiting for in-progress instance launches or terminations to complete.
    • Set WaitForTransitioningInstances to false when calling the CancelInstanceRefresh API
    • This bypasses the wait for pending instance activities such as lifecycle hooks
    • Useful during emergency situations when needing to rapidly roll forward to a new deployment
  • Rollback – Instance refresh can be rolled back using RollbackInstanceRefresh API while still in progress, which replaces instances that were already replaced during the refresh.

AWS Certification Exam Practice Questions

  • Questions are collected from Internet and the answers are marked as per my knowledge and understanding (which might differ with yours).
  • AWS services are updated everyday and both the answers and questions might be outdated soon, so research accordingly.
  • AWS exam questions are not updated to keep up the pace with AWS updates, so even if the underlying feature has changed the question might not be updated
  • Open to further feedback, discussion and correction.
  1. Your application is running on EC2 in an Auto Scaling group. Bootstrapping is taking 20 minutes to complete. You find out that instances are shown as InService although the bootstrapping has not completed. How can you make sure that new instances are not added until the bootstrapping has finished. Choose the correct answer:
    1. Create a CloudWatch alarm with an SNS topic to send alarms to your DevOps engineer.
    2. Create a lifecycle hook to keep the instance in pending:wait state until the bootstrapping has finished and then put the instance in pending:proceed state.
    3. Increase the number of instances in your Auto Scaling group.
    4. Create a lifecycle hook to keep the instance in standby state until the bootstrapping has finished and then put the instance in pending:proceed state.
  2. When a scale out event occurs, the Auto Scaling group launches the required number of EC2 instances using its assigned launch configuration. What instance state do these instances start in? Choose the correct answer:
    1. pending:wait
    2. InService
    3. Pending
    4. Terminating
  3. With AWS Auto Scaling, once we apply a hook and the action is complete or the default wait state timeout runs out, the state changes to what, depending on which hook we have applied and what the instance is doing? Select two. Choose the 2 correct answers:
    1. pending:proceed
    2. pending:wait
    3. terminating:wait
    4. terminating:proceed
  4. For AWS Auto Scaling, what is the first transition state an existing instance enters after leaving steady state in Standby mode?
    1. Detaching
    2. Terminating:Wait
    3. Pending (You can put any instance that is in an InService state into a Standby state. This enables you to remove the instance from service, troubleshoot or make changes to it, and then put it back into service. Instances in a Standby state continue to be managed by the Auto Scaling group. However, they are not an active part of your application until you put them back into service. Refer link)
    4. EnteringStandby
  5. For AWS Auto Scaling, what is the first transition state an instance enters after leaving steady state when scaling in due to health check failure or decreased load?
    1. Terminating (When Auto Scaling responds to a scale in event, it terminates one or more instances. These instances are detached from the Auto Scaling group and enter the Terminating state. Refer link)
    2. Detaching
    3. Terminating:Wait
    4. EnteringStandby
  6. A company runs a stateful application on an Auto Scaling group. The application requires that all in-progress transactions are completed before an instance is terminated. If a termination lifecycle hook fails or times out, the instance should NOT be terminated to avoid data loss. Which solution meets these requirements?
    1. Configure the lifecycle hook default result to ABANDON and use a CloudWatch alarm to notify the operations team.
    2. Set the lifecycle hook heartbeat timeout to 48 hours to provide maximum time for completion.
    3. Configure an instance lifecycle policy to retain instances when the termination lifecycle action is abandoned.
    4. Use a custom Lambda function to continuously record heartbeats and prevent timeout.
  7. An organization wants to execute a custom action when an Auto Scaling instance enters a wait state during launch. Which notification target is recommended as a best practice?
    1. Amazon SNS topic with email subscription
    2. Amazon SQS FIFO queue
    3. Amazon EventBridge rule invoking a Lambda function
    4. Amazon SQS standard queue with a polling consumer

📖 Related: AWS Auto Scaling with ELB – Integration Guide

References


Amazon CloudWatch Logs – Collection & Insights

Amazon CloudWatch Logs

  • CloudWatch Logs can be used to monitor, store, and access log files from EC2 instances, CloudTrail, Route 53, and other sources.
  • CloudWatch Logs uses the log data for monitoring with no code changes required.
  • CloudWatch Logs requires the unified CloudWatch agent to be installed on EC2 instances and on-premises servers. (Note: The older CloudWatch Logs agent is deprecated and no longer supported. Use the unified CloudWatch agent instead.)
  • The unified CloudWatch agent can collect both logs and metrics from EC2 instances and on-premises servers.
  • A VPC endpoint can be configured to keep traffic between VPC and CloudWatch Logs from leaving the Amazon network. It doesn’t require an IGW, NAT, VPN connection, or Direct Connect connection.
  • CloudWatch Logs allows exporting log data from log groups to an S3 bucket, which can then be used for custom processing and analysis, or to load onto other systems.
  • Log data is encrypted while in transit and while it is at rest.
  • Log data can be encrypted using AWS KMS customer managed keys (CMK).
  • CloudWatch Logs now supports log events up to 1 MB in size (increased from the previous 256 KB limit, as of April 2025).

Required Mainly for SysOps Associate & DevOps Professional Exam

CloudWatch Logs Concepts

Log Events

  • A log event is a record of some activity recorded by the application or resource being monitored.
  • Log event record contains two properties: the timestamp of when the event occurred, and the raw event message.

Log Streams

  • A log stream is a sequence of log events that share the same source for e.g. log events from an Apache access log on a specific host.

Log Groups

  • Log groups define groups of log streams that share the same retention, monitoring, and access control settings for e.g. Apache access logs from each host grouped through log streams into a single log group.
  • Each log stream has to belong to one log group.
  • There is no limit on the number of log streams that can belong to one log group.

Log Classes

  • CloudWatch Logs offers two log classes:
    • Standard – Full-featured log class with real-time monitoring, anomaly detection, Live Tail, Logs Insights, metric filters, subscription filters, and all CloudWatch Logs capabilities.
    • Infrequent Access (IA) – Lower-cost log class (50% lower per GB ingestion price) designed for logs that are queried occasionally, such as forensic investigations and compliance auditing. Supports Logs Insights queries, export to S3, encryption, and data protection.
  • Log class is set at log group creation time and cannot be changed.
  • Infrequent Access does not support metric filters, subscription filters, Live Tail, or anomaly detection.

Metric Filters

  • Metric filters can be used to extract metric observations from ingested events and transform them to data points in a CloudWatch metric.
  • Metric filters are assigned to log groups, and all of the filters assigned to a log group are applied to their log streams.
  • Metric filters are only available for log groups in the Standard log class.

Retention Settings

  • Retention settings can be used to specify how long log events are kept in CloudWatch Logs.
  • Expired log events get deleted automatically.
  • Retention settings are assigned to log groups, and the retention assigned to a log group is applied to their log streams.

CloudWatch Logs Features

CloudWatch Logs Insights

  • CloudWatch Logs Insights is an interactive, purpose-built query language for searching and analyzing log data.
  • Supports queries across multiple log groups and multiple AWS accounts.
  • Automatically discovers fields in JSON-format logs and generates visualizations.
  • Supports OpenSearch SQL and PPL (Piped Processing Language) directly within the Logs Insights console for SQL-based log analytics and JOIN operations across log groups (launched Dec 2024).
  • Field Indexes (Nov 2024) – Index critical log attributes (e.g., requestId, transactionId) to accelerate query performance and reduce scan volume. Up to 20 fields can be indexed per log group. Available at no additional cost.
  • AI-Powered Natural Language Query Generation (June 2024) – Generate Logs Insights queries using plain language, powered by generative AI.
  • Scheduled Queries (Nov 2025) – Automate log analysis by running Logs Insights queries on a recurring schedule, delivering results to S3 or EventBridge.
  • 23 New Query Commands and Functions (June 2026) – Includes hash functions (md5, sha256), string functions (strcontains with case-insensitive search, split), conditional logic (if statement), conversion functions (toNumber, toInt, toLong, toDouble), CSV/XML parsing, histogram, and multi-stage pipes for stats.
  • Facets (June 2026) – Explore log data visually without writing a query for interactive log exploration.
  • Lookup Tables (June 2026) – Enrich query results with external metadata.
  • Parameterized Queries (June 2026) – Save reusable query templates with fill-in variables.
  • JOIN and Sub-queries (June 2026) – Correlate data across log groups in a single query.

Live Tail

  • Live Tail (launched June 2023) provides real-time streaming of log events as they are ingested into log groups.
  • Helps quickly view, filter, and troubleshoot issues in incoming logs without writing queries.
  • Supports fine-grained controls to filter and highlight attributes of interest, and pause/replay logs.
  • A Live Tail session can last for up to 3 hours.
  • Available via console, CLI (streaming support added June 2024), and API.
  • Integrated natively into the AWS Lambda console for real-time function log visibility (Oct 2024).
  • Only available for Standard log class.

Anomaly Detection and Pattern Analytics

  • Anomaly Detection (launched Nov 2023) uses machine learning algorithms trained on decades of Amazon and AWS operational data to automatically identify anomalies in log data.
  • Anomaly detectors train on the past two weeks of log events (training takes up to 15 minutes) and then continuously analyze incoming logs.
  • Default quota: up to 500 anomaly detectors per account (increased from 10 in Oct 2024).
  • Pattern Analytics automatically recognizes and clusters patterns among log records, extracting noteworthy content and trends.
  • Pattern and diff commands use named tokens for easier-to-read results.
  • Only available for Standard log class.

Log Transformation and Enrichment

  • Log Transformation (launched Nov 2024) normalizes logs into a consistent format at the time of ingestion.
  • Supports pre-configured templates for common AWS services (WAF, VPC Flow Logs) and custom transformers (Grok patterns).
  • Each transformer can extract up to 200 fields from a log event.
  • Transformed logs can be leveraged for field indexes, discovered fields in Logs Insights, metric filters, and subscription filters.
  • Included with existing Standard log class ingestion price (no additional cost for transformation).
  • Supports OCSF (Open Cybersecurity Schema Framework) and OTel format conversion for security and compliance data.

Log Analytics (Unified Console)

  • Log Analytics (launched June 2026) is a unified console experience that brings together:
    • CloudWatch Logs Insights for querying and analyzing log data
    • Live Tail for real-time log streaming
    • Contributor Insights for identifying top contributors
  • Supports multiple queries in different tabs simultaneously.
  • Combines facets, saved queries with parameters, natural language query generation, and visualizations in a single interface.

CloudWatch Logs Use Cases

Monitor Logs from EC2 Instances in Real-time

  • Can help monitor applications and systems using log data.
  • Can help track number of errors for e.g. 404, 500, or even specific literal terms “NullReferenceException”, occurring in applications, which can then be matched to a threshold to send notification.

Monitor AWS CloudTrail Logged Events

  • Can be used to monitor particular API activity as captured by CloudTrail by creating alarms in CloudWatch and receiving notifications.

Archive Log Data

  • Can help store log data in highly durable storage, an alternative to S3.
  • Log retention setting can be modified, so that any log events older than this setting are automatically deleted.

Log Route 53 DNS Queries

  • Can help log information about the DNS queries that Route 53 receives.

Managed Syslog Ingestion

  • Managed Syslog Ingestion (launched June 2026) enables sending syslog messages from firewalls, routers, switches, and Linux servers directly into CloudWatch Logs.
  • Eliminates the need for custom syslog collection infrastructure.

Real-time Processing of Log Data with Subscriptions

  • Subscriptions provide access to a real-time feed of log events from CloudWatch Logs and deliver them to other services such as Kinesis Data Streams, Amazon Data Firehose, AWS Lambda, or Amazon OpenSearch Service for custom processing, analysis, or loading to other systems.
  • A subscription filter defines the filter pattern to use for filtering which log events get delivered, as well as the destination for matching log events.
  • CloudWatch Logs log group can be configured to stream data to an Amazon OpenSearch Service cluster in near real-time. (Note: Amazon Elasticsearch Service was renamed to Amazon OpenSearch Service in September 2021.)
  • Account-Level Subscription Filters (Jan 2024) – Deliver real-time log events from all log groups in an account to a Kinesis Data Stream, Amazon Data Firehose, or Lambda using a single account-level filter (one per account per Region).

Cross-Account and Cross-Region Log Centralization

  • Cross-Account Observability enables searching log groups across multiple accounts, running cross-account Logs Insights queries, and creating Contributor Insights rules.
  • Cross-Account and Cross-Region Log Centralization (Sept 2025) copies log data from multiple AWS accounts and regions into a single destination account for centralized management.

Searching and Filtering

  • CloudWatch Logs allows searching and filtering the log data by creating one or more metric filters.
  • Metric filters define the terms and patterns to look for in log data as it is sent to CloudWatch Logs.
  • CloudWatch Logs uses these metric filters to turn log data into numerical CloudWatch metrics that can be graphed or used to set alarms.

AWS Certification Exam Practice Questions

  • Questions are collected from Internet and the answers are marked as per my knowledge and understanding (which might differ with yours).
  • AWS services are updated everyday and both the answers and questions might be outdated soon, so research accordingly.
  • AWS exam questions are not updated to keep up the pace with AWS updates, so even if the underlying feature has changed the question might not be updated
  • Open to further feedback, discussion and correction.
  1. Once we have our logs in CloudWatch, we can do a number of things such as: Choose 3. Choose the 3 correct answers:[CDOP]
    1. Send the log data to AWS Lambda for custom processing or to load into other systems
    2. Stream the log data to Amazon Kinesis
    3. Stream the log data into Amazon OpenSearch Service in near real-time with CloudWatch Logs subscriptions.
    4. Record API calls for your AWS account and delivers log files containing API calls to your Amazon S3 bucket
  2. You have decided to set the threshold for errors on your application to a certain number and once that threshold is reached you need to alert the Senior DevOps engineer. What is the best way to do this? Choose 3. Choose the 3 correct answers: [CDOP]
    1. Set the threshold your application can tolerate in a CloudWatch Logs group and link a CloudWatch alarm on that threshold.
    2. Use the unified CloudWatch agent to send log data from the app to CloudWatch Logs from Amazon EC2 instances
    3. Pipe data from EC2 to the application logs using AWS Data Pipeline and CloudWatch
    4. Once a CloudWatch alarm is triggered, use SNS to notify the Senior DevOps Engineer.
  3. You are hired as the new head of operations for a SaaS company. Your CTO has asked you to make debugging any part of your entire operation simpler and as fast as possible. She complains that she has no idea what is going on in the complex, service-oriented architecture, because the developers just log to disk, and it’s very hard to find errors in logs on so many services. How can you best meet this requirement and satisfy your CTO? [CDOP]
    1. Copy all log files into AWS S3 using a cron job on each instance. Use an S3 Notification Configuration on the PutBucket event and publish events to AWS Lambda. Use the Lambda to analyze logs as soon as they come in and flag issues. (is not fast in search and introduces delay)
    2. Begin using CloudWatch Logs on every service. Stream all Log Groups into S3 objects. Use AWS EMR cluster jobs to perform adhoc MapReduce analysis and write new queries when needed. (is not fast in search and introduces delay)
    3. Copy all log files into AWS S3 using a cron job on each instance. Use an S3 Notification Configuration on the PutBucket event and publish events to AWS Kinesis. Use Apache Spark on AWS EMR to perform at-scale stream processing queries on the log chunks and flag issues. (is not fast in search and introduces delay)
    4. Begin using CloudWatch Logs on every service. Stream all Log Groups into an Amazon OpenSearch Service domain running OpenSearch Dashboards and perform log analysis on a search cluster. (OpenSearch with Dashboards (formerly ELK – Elasticsearch, Kibana stack) is designed specifically for real-time, ad-hoc log analysis and aggregation)
  4. You use Amazon CloudWatch as your primary monitoring system for your web application. After a recent software deployment, your users are getting Intermittent 500 Internal Server Errors when using the web application. You want to create a CloudWatch alarm, and notify an on-call engineer when these occur. How can you accomplish this using AWS services? (Choose three.) [CDOP]
    1. Deploy your web application as an AWS Elastic Beanstalk application. Use the default Elastic Beanstalk CloudWatch metrics to capture 500 Internal Server Errors. Set a CloudWatch alarm on that metric.
    2. Install the unified CloudWatch agent on your servers to stream web application logs to CloudWatch.
    3. Use Amazon Simple Email Service to notify an on-call engineer when a CloudWatch alarm is triggered.
    4. Create a CloudWatch Logs group and define metric filters that capture 500 Internal Server Errors. Set a CloudWatch alarm on that metric.
    5. Use Amazon Simple Notification Service to notify an on-call engineer when a CloudWatch alarm is triggered.
    6. Use AWS Data Pipeline to stream web application logs from your servers to CloudWatch.
  5. A company needs to consolidate logs from multiple AWS accounts for compliance auditing but wants to minimize costs since logs are only queried during investigations. Which CloudWatch Logs approach is most cost-effective? [SAA/SysOps]
    1. Use Standard log class with metric filters for all log groups
    2. Use Infrequent Access log class for the log groups and query with Logs Insights when needed
    3. Export all logs to S3 immediately and use Athena for queries
    4. Use Live Tail to monitor logs in real-time across accounts
  6. A DevOps team wants to quickly identify anomalous log patterns after a deployment without writing custom detection rules. Which CloudWatch Logs feature should they use? [CDOP]
    1. Metric filters with CloudWatch Alarms
    2. CloudWatch Logs Insights scheduled queries
    3. CloudWatch Logs Anomaly Detection with pattern analytics
    4. Subscription filters to Lambda for custom processing
  7. A team needs to stream log events from ALL log groups in their AWS account to a central Kinesis Data Stream without creating individual subscription filters for each log group. What should they use? [CDOP]
    1. Cross-account observability with a monitoring account
    2. CloudWatch Logs transformation with Kinesis destination
    3. Account-level subscription filter policy
    4. CloudWatch Logs Live Tail with CLI streaming
  8. An engineer wants to speed up CloudWatch Logs Insights queries that frequently filter by requestId across large log groups. Which feature should they configure? [CDOP/SysOps]
    1. Log transformation with Grok patterns
    2. Field indexes on the requestId field
    3. Infrequent Access log class for the log group
    4. Scheduled queries with S3 delivery

References

AWS OpsWorks Deployment Strategies – Certification

⚠️ SERVICE DEPRECATED – IMPORTANT NOTICE

AWS OpsWorks Stacks reached End of Life (EOL) on May 26, 2024. All OpsWorks services (Stacks, Chef Automate, and Puppet Enterprise) have been disabled for both new and existing customers.

This content is maintained for historical reference and for understanding deployment strategies that remain applicable to modern AWS services.

Recommended Migration Paths:

For migration guidance: Migrate OpsWorks to Systems Manager

AWS OpsWorks Deployment Strategies (Historical Reference)

NOTE: OpsWorks was deprecated in 2024. These deployment strategy concepts remain relevant for the DevOps Professional Exam using modern services (CodeDeploy, ECS, Systems Manager).

The deployment strategies described below (All at Once, Rolling, Blue/Green) are foundational concepts that apply across modern AWS services like CodeDeploy, ECS, EKS, and Elastic Beanstalk.

All at Once Deployment

  • OpsWorks Stacks did not automatically deploy updated code to online instances, requiring manual deployment
  • Deploy command (for apps) or Update Custom Cookbooks command (for cookbooks) deployed the update to every instance concurrently
  • Approach was simple and fast, but led to downtime in case of error
  • OpsWorks allowed rollback to restore previously deployed app version
  • By default, AWS OpsWorks Stacks stored the five most recent deployments, allowing rollback up to four versions

Modern Equivalent

  • AWS CodeDeploy – All-at-once deployment configuration with automatic rollback on CloudWatch alarm triggers
  • Amazon ECS – Rolling updates with minimumHealthyPercent=0 and maximumPercent=100 achieves all-at-once behavior

Rolling Deployment

  • A rolling deployment updates an application on instances in multiple phases.
  • With each phase, a subset of the online instances is updated and verified before starting the next phase.
  • In case of issues, instances running the old version continue handling incoming traffic until issues are resolved.
  • Steps to perform Rolling deployment:
    • Deploy the app on a single application server instance
    • Deregister the instance from the load balancer to prevent it from serving traffic
    • Verify the app is working fine
    • Deploy the update on the remainder of instances

Modern Equivalent

  • AWS CodeDeploy – Rolling deployments with configurable batch sizes, health checks, and automatic rollback
  • Amazon ECS – Default rolling update with minimumHealthyPercent and maximumPercent parameters
  • Amazon EKS – Kubernetes native rolling updates with maxSurge and maxUnavailable
  • Elastic Beanstalk – Rolling deployment policy with configurable batch size

Blue Green Deployment

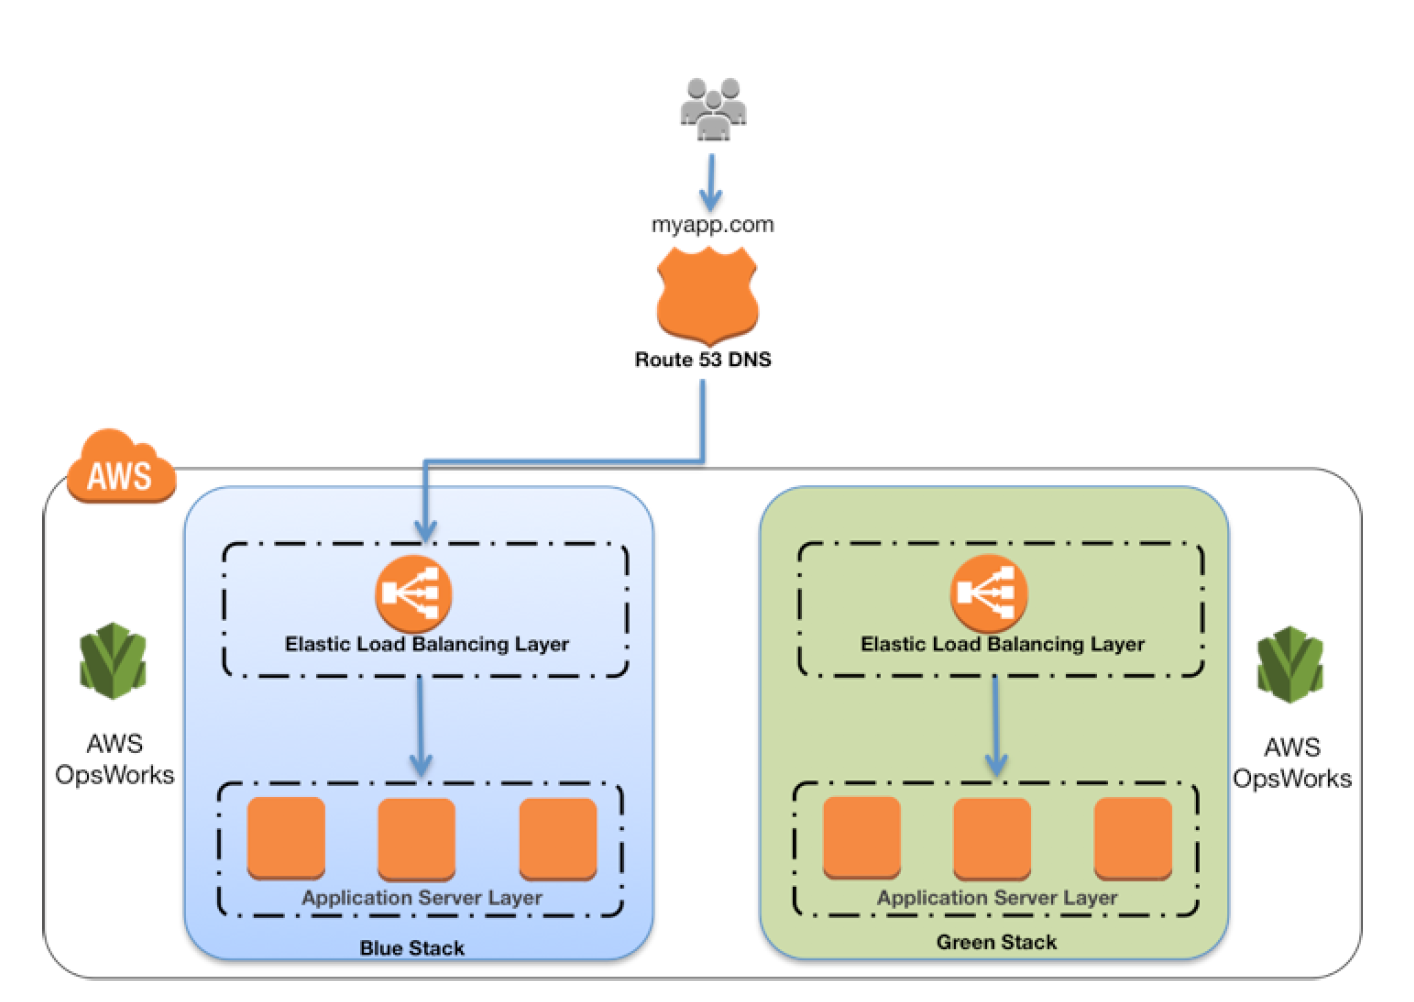
  • Blue Green deployment uses separate environments for each phase of the application’s lifecycle.
    • Blue environment is the production environment hosting the current application.
    • Green environment is the staging environment hosting the updated application.
  • Development and testing can be performed on non-publicly-accessible environments, and traffic switched when ready.
  • Steps for Blue Green deployment with Route 53 and ELB:
    • Attach unused ELB to the green environment’s application server layer
    • After green instances pass ELB health checks, adjust Route 53 weights to route traffic gradually from Blue to Green
    • Once Green is ready to handle all traffic, detach the load balancer from the Blue environment
    • Retain Blue environment for rollback capability

OpsWorks Blue Green Deployment

Modern Equivalent

  • Amazon ECS (Native) – Built-in blue/green deployments launched July 2025, no CodeDeploy dependency required
  • AWS CodeDeploy – Blue/green deployment for EC2, Lambda, and ECS with traffic shifting
  • Elastic Beanstalk – Blue/green via environment cloning and CNAME swap
  • Route 53 – Weighted routing policies for gradual traffic shifting
  • Application Load Balancer – Target group weighting for blue/green deployments

Modern AWS Deployment Strategies (2025-2026)

With OpsWorks deprecated, AWS now offers more powerful and integrated deployment capabilities across multiple services.

AWS CodeDeploy

  • Fully managed deployment service automating software deployments to EC2, Lambda, ECS, and on-premises servers
  • Deployment strategies: All-at-once, Rolling, Blue/Green, Canary, Linear
  • Automatic rollback on deployment failure or CloudWatch alarm triggers
  • Integration with CI/CD pipelines via CodePipeline
  • Lifecycle event hooks for custom validation at each deployment stage
  • For ECS, CodeDeploy is being superseded by ECS-native deployments for new workloads

Amazon ECS Native Deployments (New – 2025)

  • Built-in Blue/Green (July 2025) – ECS now supports blue/green deployments natively without requiring CodeDeploy
    • Deployment lifecycle hooks for custom testing during deployment
    • Dark Canary deployments for testing with production traffic shadows
    • Automatic rollback on CloudWatch alarm breaches
  • Canary Deployments (October 2025) – Route a small percentage of traffic (as low as 0.1%) to the new revision, monitor during bake time, then complete the shift
  • Linear Deployments (October 2025) – Shift traffic in equal increments (minimum 3%) with configurable bake time between each shift
  • Supports ALB and NLB (NLB support added February 2026)
  • Integrated with CloudWatch alarms for automatic deployment stop/rollback
  • ECS-native is now the recommended default for new ECS deployments over CodeDeploy

AWS Systems Manager

  • Unified interface for managing AWS resources – direct replacement for OpsWorks configuration management
  • State Manager for configuration management and compliance
  • Automation runbooks for common operational tasks
  • Patch Manager for automated OS and application patching
  • Run Command for executing commands across fleet of instances

Amazon EKS Deployment Strategies

  • Kubernetes native rolling updates with fine-grained control
  • Blue/green using service mesh (Istio, App Mesh successor) or ingress controller
  • Canary deployments with Argo Rollouts or Flagger
  • GitOps workflows with ArgoCD or Flux

AWS App Runner

  • Fully managed service for containerized web applications
  • Automatic deployments from source code or container images
  • Built-in load balancing, auto-scaling, and zero-downtime deployments
  • No infrastructure management required

Deployment Strategy Comparison

Strategy Downtime Rollback Speed Risk AWS Services
All at Once Yes (if failure) Slow High CodeDeploy, Elastic Beanstalk
Rolling No Medium Medium CodeDeploy, ECS, EKS, Beanstalk
Blue/Green No Fast Low CodeDeploy, ECS (native), Beanstalk, Route 53
Canary No Fast Lowest CodeDeploy, ECS (native), Lambda
Linear No Fast Low CodeDeploy, ECS (native), Lambda

AWS Certification Exam Practice Questions

⚠️ EXAM NOTE: AWS OpsWorks is still listed as an in-scope service for the DOP-C02 (DevOps Professional) exam as of 2026. However, questions are expected to focus on understanding the service’s deprecation and migration to modern alternatives. Focus study efforts on CodeDeploy, ECS deployment strategies, and Systems Manager.

  • Questions are collected from Internet and the answers are marked as per my knowledge and understanding (which might differ with yours).
  • AWS services are updated everyday and both the answers and questions might be outdated soon, so research accordingly.
  • AWS exam questions are not updated to keep up the pace with AWS updates, so even if the underlying feature has changed the question might not be updated
  • Open to further feedback, discussion and correction.

Historical OpsWorks Questions

  1. You company runs a complex customer relations management system that consists of around 10 different software components all backed by the same Amazon Relational Database (RDS) database. You adopted AWS OpsWorks to simplify management and deployment of that application and created an AWS OpsWorks stack with layers for each of the individual components. An internal security policy requires that all instances should run on the latest Amazon Linux AMI and that instances must be replaced within one month after the latest Amazon Linux AMI has been released. AMI replacements should be done without incurring application downtime or capacity problems. You decide to write a script to be run as soon as a new Amazon Linux AMI is released. Which solutions support the security policy and meet your requirements? Choose 2 answers
    1. Assign a custom recipe to each layer, which replaces the underlying AMI. Use AWS OpsWorks life-cycle events to incrementally execute this custom recipe and update the instances with the new AMI. (AMI cannot be updated using recipes)
    2. Create a new stack and layers with identical configuration, add instances with the latest Amazon Linux AMI specified as a custom AMI to the new layer, switch DNS to the new stack, and tear down the old stack. (Blue-Green Deployment)
    3. Identify all Amazon Elastic Compute Cloud (EC2) instances of your AWS OpsWorks stack, stop each instance, replace the AMI ID property with the ID of the latest Amazon Linux AMI ID, and restart the instance. To avoid downtime, make sure not more than one instance is stopped at the same time. (Instances cannot be updated by updating the AMI id and needs to be launched anew)
    4. Specify the latest Amazon Linux AMI as a custom AMI at the stack level, terminate instances of the stack and let AWS OpsWorks launch new instances with the new AMI. (Would result in downtime)
    5. Add new instances with the latest Amazon Linux AMI specified as a custom AMI to all AWS OpsWorks layers of your stack, and terminate the old ones. (Disposable Rolling deployment)
  2. A company has developed a Ruby on Rails content management platform. Currently, OpsWorks with several stacks for dev, staging, and production is being used to deploy and manage the application. Now the company wants to start using Python instead of Ruby. How should the company manage the new deployment?
    1. Update the existing stack with Python application code and deploy the application using the deploy life-cycle action to implement the application code.
    2. Create a new stack that contains a new layer with the Python code. To cut over to the new stack the company should consider using Blue/Green deployment
    3. Create a new stack that contains the Python application code and manage separate deployments of the application via the secondary stack using the deploy lifecycle action to implement the application code.
    4. Create a new stack that contains the Python application code and manages separate deployments of the application via the secondary stack

Modern Deployment Strategy Questions

  1. A company is migrating from AWS OpsWorks to a modern deployment solution. Their application runs on Amazon ECS with Fargate. They want to deploy updates with minimal risk, routing only 10% of traffic to the new version initially, monitoring for 10 minutes, then completing the shift. Which deployment strategy should they use?
    1. ECS rolling update with minimumHealthyPercent set to 90%
    2. ECS native canary deployment with a 10% initial traffic shift and 10-minute bake time
    3. AWS CodeDeploy blue/green deployment with a 10-minute wait time
    4. ECS native linear deployment with 10% increments

    Answer: B – ECS native canary deployment (launched October 2025) allows routing a small percentage of traffic to the new revision with a configurable bake time before completing the shift. This matches the requirement of 10% initial traffic with monitoring.

  2. A DevOps engineer needs to implement a deployment strategy for an ECS service that shifts traffic in 5 equal increments over 25 minutes. Which approach is most appropriate?
    1. AWS CodeDeploy with a custom linear deployment configuration
    2. ECS native linear deployment with 20% increments and 5-minute bake time
    3. ECS blue/green deployment with Route 53 weighted routing
    4. ECS rolling update with maximum percent set to 120%

    Answer: B – ECS native linear deployments (October 2025) shift traffic in equal increments with bake time between each shift. 5 increments of 20% with 5-minute bake times achieves the 25-minute gradual shift requirement. For new ECS deployments, ECS-native is preferred over CodeDeploy.

  3. A company previously managed configuration and deployments using AWS OpsWorks Stacks with custom Chef cookbooks. Now that OpsWorks has reached EOL, which combination of services provides equivalent functionality? (Choose 2)
    1. AWS Elastic Beanstalk with custom platform hooks
    2. AWS Systems Manager State Manager with custom SSM documents
    3. AWS Config rules with auto-remediation
    4. AWS CodeDeploy with AppSpec lifecycle hooks
    5. Amazon Inspector with automated patching

    Answers: B, D – Systems Manager State Manager replaces OpsWorks configuration management (cookbooks → SSM documents), and CodeDeploy replaces OpsWorks deployment commands with AppSpec lifecycle hooks providing similar customization to Chef recipes.

  4. An organization wants to implement blue/green deployments for their ECS services. They are evaluating ECS-native blue/green versus CodeDeploy-managed blue/green. Which statement is correct about ECS-native blue/green deployments?
    1. ECS-native blue/green requires a separate CodeDeploy application and deployment group
    2. ECS-native blue/green only supports ALB, not NLB
    3. ECS-native blue/green supports deployment lifecycle hooks for custom testing without requiring CodeDeploy
    4. ECS-native blue/green does not support automatic rollback on CloudWatch alarms

    Answer: C – ECS native blue/green (July 2025) operates entirely within ECS without CodeDeploy dependency. It supports lifecycle hooks for custom testing, CloudWatch alarm-based rollback, and both ALB and NLB (NLB support added February 2026).

References

AWS Certified Cloud Practitioner (CLF-C01) Exam Learning Path

AWS Certified Cloud Practitioner (CLF-C02) Exam Learning Path

📋 Exam Update: The AWS Certified Cloud Practitioner exam was updated to CLF-C02 on September 19, 2023. The previous version (CLF-C01) was retired on September 18, 2023. This guide has been fully updated for the CLF-C02 exam.

  • AWS Certified Cloud Practitioner (CLF-C02) is a foundational-level certification that validates overall knowledge of the AWS Cloud, independent of a specific job role.
  • AWS Certified Cloud Practitioner exam is ideal for starting your AWS certification journey and provides non-technical professionals foundational cloud literacy.
  • AWS Certified Cloud Practitioner Exam has 65 questions to be answered in 90 minutes.
  • A scaled score of 700 out of 1000 is required to pass. Approximately 50 questions are scored, while 15 are unscored pretest questions.
  • The exam can be taken at a Pearson VUE testing center or via online proctoring from any private space (home or office).
  • The exam costs $100 USD and is available in multiple languages including English, Japanese, Korean, and Simplified Chinese.

AWS Certified Cloud Practitioner exam validates the following:

  • Define what the AWS Cloud is and the basic global infrastructure
  • Describe the AWS Cloud value proposition and benefits of cloud migration
  • Describe key services on the AWS platform and their common use cases (compute, storage, networking, databases, AI/ML)
  • Describe basic security and compliance aspects of the AWS platform and the shared responsibility model
  • Define the billing, account management, and pricing models
  • Identify sources of documentation or technical assistance (e.g., white papers, support plans)
  • Describe basic/core characteristics of deploying and operating in the AWS Cloud
  • Identify cloud migration strategies and AWS migration services

Refer to the AWS Certified Cloud Practitioner (CLF-C02) Exam Guide

CLF-C02 Exam Domain Breakdown

Domain Weight
Domain 1: Cloud Concepts 24%
Domain 2: Security and Compliance 30%
Domain 3: Cloud Technology and Services 34%
Domain 4: Billing, Pricing, and Support 12%

Key Changes from CLF-C01 to CLF-C02:

  • Security and Compliance weight increased from 25% to 30%
  • Billing and Pricing weight decreased from 16% to 12%
  • New topics added: AI/ML services, cloud migration strategies, sustainability pillar
  • Greater emphasis on the AWS Well-Architected Framework (now 6 pillars)
  • Exam time reduced from 100 minutes to 90 minutes

AWS Certified Cloud Practitioner Exam Resources

AWS Cloud Computing Whitepapers

AWS Certified Cloud Practitioner (CLF-C02) Exam Contents

Domain 1: Cloud Concepts (24%)

  • 1.1 Define the benefits of the AWS Cloud
    • Agility – Speed, Experimentation, Innovation
    • Elasticity – Scale on demand, Eliminate wasted capacity
    • High Availability – Spread across multiple Availability Zones
    • Flexibility – Broad set of products, Low to no cost to entry
    • Security – Compliance certifications, Shared responsibility model
    • Global Reach – Deploy globally in minutes using Regions and Edge Locations
  • 1.2 Identify design principles of the AWS Cloud
    • Advantages of Cloud Computing
      • Trade upfront expense for variable expense
      • Benefit from massive economies of scale
      • Stop guessing about capacity
      • Increase speed and agility
      • Stop spending money running and maintaining data centers
      • Go global in minutes
    • AWS Well-Architected Framework (6 Pillars)
      • Operational Excellence – Run and monitor systems to deliver business value
      • Security – Protect information, systems, and assets
      • Reliability – Recover from failures and meet demand
      • Performance Efficiency – Use resources efficiently
      • Cost Optimization – Avoid unnecessary costs
      • Sustainability – Minimize environmental impact of cloud workloads (added 2021)
  • 1.3 Understand the benefits of and strategies for migration to the AWS Cloud
    • Cloud adoption strategies (AWS Cloud Adoption Framework – CAF)
    • Migration strategies: the 7 Rs (Rehost, Replatform, Repurchase, Refactor, Retire, Retain, Relocate)
    • AWS Cloud Architecting – Best Practices
  • 1.4 Understand concepts of cloud economics
    • Total Cost of Ownership (TCO) – Compare on-premises vs. cloud costs
    • Fixed costs vs. variable costs
    • Right-sizing and resource optimization
    • Managed services reduce operational overhead

Domain 2: Security and Compliance (30%)

  • 2.1 Define the AWS Shared Responsibility Model
    • AWS responsibility: Security OF the cloud (hardware, software, networking, facilities)
    • Customer responsibility: Security IN the cloud (data, identity, applications, OS, network config)
    • Shared controls: Patch management, configuration management, awareness & training
  • 2.2 Define AWS Cloud security and compliance concepts
    • AWS compliance programs (SOC, PCI DSS, HIPAA, FedRAMP)
    • Data protection and encryption (at rest and in transit)
    • AWS Artifact – on-demand access to AWS compliance reports
  • 2.3 Identify AWS access management capabilities
    • IAM – Users, Groups, Roles, Policies
    • Multi-Factor Authentication (MFA)
    • IAM Identity Center (formerly AWS SSO) – centralized access management
    • Root user vs. IAM user best practices
  • 2.4 Identify components and resources for security
    • CloudTrail – API call auditing and logging
    • AWS GuardDuty – intelligent threat detection
    • AWS Inspector – automated vulnerability assessment
    • AWS Security Hub – centralized security findings
    • AWS Shield – DDoS protection
    • WAF – Web Application Firewall
    • AWS KMS – Key Management Service for encryption
    • AWS Macie – sensitive data discovery using ML

Domain 3: Cloud Technology and Services (34%)

  • 3.1 Define methods of deploying and operating in the AWS Cloud
    • Deployment models: Cloud, Hybrid, On-premises (private cloud)
    • Connectivity options: VPN, Direct Connect, Public internet
    • AWS Management Console, CLI, SDKs, Infrastructure as Code
  • 3.2 Define the AWS global infrastructure
    • Regions, Availability Zones, Edge Locations, Local Zones, Wavelength Zones
    • Factors for choosing a Region (compliance, latency, service availability, cost)
  • 3.3 Identify AWS compute services
    • EC2 – Virtual servers, instance types, pricing models
    • Lambda – Serverless compute, event-driven
    • ECS & EKS – Container orchestration
    • AWS Fargate – Serverless containers
    • Elastic Beanstalk – Platform as a Service (PaaS)
    • AWS Lightsail – Simple virtual private servers
    • Auto Scaling – Scale based on demand
  • 3.4 Identify AWS storage services
    • S3 – Object storage, storage classes (Standard, IA, Glacier, Glacier Deep Archive)
    • EBS – Block storage for EC2
    • EFS – Shared file storage (NFS)
    • FSx – Managed file systems (Windows, Lustre, NetApp, OpenZFS)
    • AWS Storage Gateway – Hybrid cloud storage
    • S3 Glacier – Archival long-term storage
  • 3.5 Identify AWS networking services
    • VPC – Virtual private network, subnets, security groups, NACLs
    • CloudFront – Content delivery network (CDN)
    • Route 53 – DNS and domain registration, routing policies
    • ELB – Distribute traffic (ALB, NLB, GLB)
    • VPN & Direct Connect – On-premises connectivity
    • AWS Global Accelerator – Improve application availability and performance
    • AWS Transit Gateway – Connect VPCs and on-premises networks
  • 3.6 Identify AWS database services
    • RDS – Managed relational databases (MySQL, PostgreSQL, MariaDB, Oracle, SQL Server)
    • Aurora – High-performance MySQL/PostgreSQL compatible
    • DynamoDB – Managed NoSQL (key-value and document)
    • ElastiCache – In-memory caching (Redis, Memcached)
    • Amazon Redshift – Data warehouse
    • Amazon DocumentDB – MongoDB compatible
    • Amazon Neptune – Graph database
  • 3.7 Identify AWS AI/ML and analytics services
    • Amazon SageMaker – Build, train, and deploy ML models
    • Amazon Rekognition – Image and video analysis
    • Amazon Comprehend – Natural language processing
    • Amazon Lex – Conversational AI (chatbots)
    • Amazon Polly – Text-to-speech
    • Amazon Transcribe – Speech-to-text
    • Amazon Translate – Language translation
    • Amazon Bedrock – Generative AI with foundation models
    • Amazon Q – AI assistant for business and development
    • Amazon Athena – Serverless query service for S3
    • Amazon QuickSight – Business intelligence and dashboards
  • 3.8 Identify AWS management and governance services
  • 3.9 Identify AWS migration and transfer services
    • AWS Migration Hub – Track migrations
    • AWS Database Migration Service (DMS) – Database migration
    • AWS Snow Family (Snowcone, Snowball, Snowmobile) – Offline data transfer
    • AWS DataSync – Online data transfer
    • AWS Application Migration Service – Lift-and-shift migrations
  • 3.10 Identify messaging and integration services
    • SQS – Message queuing
    • SNS – Pub/sub notifications
    • Amazon EventBridge – Serverless event bus
    • AWS Step Functions – Workflow orchestration

Domain 4: Billing, Pricing, and Support (12%)

  • 4.1 Compare and contrast the various pricing models for AWS
    • includes AWS Pricing
      • Know EC2 pricing models: On-Demand, Reserved Instances, Savings Plans, Spot, Dedicated
      • Know Lambda pricing: based on number of requests and duration
      • Know S3 pricing: storage class, requests, data transfer
      • Understand Savings Plans (Compute and EC2 Instance) as flexible alternative to Reserved Instances
  • 4.2 Understand resources for billing, budget, and cost management
    • includes Billing and Cost Management
    • AWS Pricing Calculator – Estimate costs for AWS services and architectures
    • AWS Cost Explorer – Visualize, understand, and forecast spending
    • AWS Budgets – Set custom cost and usage budgets with alerts
    • AWS Cost and Usage Report – Most detailed billing data
    • AWS Free Tier – Explore services at no cost (Always Free, 12 Months Free, Trials)
  • 4.3 Identify AWS support resources

⚠️ AWS Support Plans Update (December 2025): AWS announced a restructuring of Support Plans at re:Invent 2025. The legacy Developer, Business, and Enterprise On-Ramp plans will be discontinued on January 1, 2027. The new structure is:

  • Business Support+ – AI-powered assistance with seamless transition to AWS experts
  • Enterprise Support – Designated TAM, 15-minute critical response, strategic guidance
  • Unified Operations – Most comprehensive, for large-scale enterprise operations

The CLF-C02 exam may still reference the current (legacy) support plan structure during the transition period.

Current AWS Support Plans (for CLF-C02 exam)

  • Basic (Free) – Account and billing support, AWS Health Dashboard, limited Trusted Advisor checks
  • Developer – Email support during business hours, 1 primary contact
  • Business – 24/7 phone/chat/email, full Trusted Advisor, AWS Support API, unlimited contacts
  • Enterprise On-Ramp – Pool of TAMs, concierge support, 30-minute critical response SLA
  • Enterprise – Dedicated TAM, Well-Architected Reviews, Concierge, <15 minute critical response SLA

Key exam points:

  • Business and above provide: 24/7 access to Cloud Support Engineers via phone/chat/email, Full Trusted Advisor checks
  • Enterprise only provides: Dedicated TAM, Well-Architected Reviews, Support Concierge, <15 min SLA

Deprecated Tool Note

The AWS TCO Calculator referenced in older study materials has been deprecated. Use the AWS Pricing Calculator instead for estimating costs and comparing on-premises vs. cloud economics.

AWS Services Overview – Whitepaper – Certification

AWS Services Overview

AWS consists of many cloud services that can be used in combinations tailored to meet business or organizational needs. This section introduces the major AWS services by category.


NOTE – This post provides a brief overview of AWS services. It is a good introduction to start all certifications. However, it is most relevant and important for the AWS Cloud Practitioner Certification Exam.

Last updated: June 2026. Reflects current AWS service names, deprecations, and new services launched through 2024-2026.


Common Features

  • Almost all features can be access-controlled through AWS Identity and Access Management (IAM)
  • Services managed by AWS are all made Scalable and Highly Available, without any changes needed from the user
  • Most services support encryption at rest and in transit by default

AWS Access

AWS allows accessing its services through unified tools using

  • AWS Management Console – a simple and intuitive user interface
  • AWS Command Line Interface (CLI) – programmatic access through scripts
  • AWS Software Development Kits (SDKs) – programmatic access through Application Program Interface (API) tailored for programming languages (Java, .NET, Node.js, PHP, Python, Ruby, Go, C++, Rust, Kotlin, Swift) or platforms (Android, Browser, iOS)
  • AWS CloudShell – a browser-based shell environment pre-authenticated with console credentials
  • Infrastructure as Code (IaC) – AWS CloudFormation, AWS CDK, or Terraform for declarative resource provisioning

Security, Identity, and Compliance

AWS Identity and Access Management (IAM)

  • enables you to securely control access to AWS services and resources for the users.
  • allows creation of AWS users, groups and roles, and use permissions to allow and deny their access to AWS resources
  • helps manage IAM users and their access with individual security credentials like access keys, passwords, and multi-factor authentication devices, or request temporary security credentials
  • helps role creation & manage permissions to control which operations can be performed by which entity, or AWS service, that assumes the role
  • enables identity federation to allow existing identities in the enterprise to access AWS without the need to create an IAM user for each identity.
  • IAM Identity Center (formerly AWS SSO) provides centralized workforce identity management and single sign-on access to multiple AWS accounts and applications.

Amazon Inspector

  • is an automated vulnerability management service that continually scans workloads for software vulnerabilities and unintended network exposure.
  • automatically discovers and scans EC2 instances, container images in Amazon ECR, and AWS Lambda functions.
  • supports both agent-based and agentless scanning for EC2 instances.
  • produces a detailed list of security findings prioritized by a contextualized risk score that correlates CVE information with network access and exploitability factors.
  • integrates with AWS Security Hub for centralized findings management.

AWS Certificate Manager

  • helps provision, manage, and deploy Secure Sockets Layer/Transport Layer Security (SSL/TLS) certificates for use with AWS services like ELB, CloudFront, and API Gateway
  • removes the time-consuming manual process of purchasing, uploading, and renewing SSL/TLS certificates.

AWS CloudHSM

  • helps meet corporate, contractual, and regulatory compliance requirements for data security by using dedicated Hardware Security Module (HSM) appliances within the AWS Cloud.
  • allows protection of encryption keys within HSMs, designed and validated to government standards for secure key management.
  • helps comply with strict key management requirements without sacrificing application performance.

AWS Directory Service

  • provides Microsoft Active Directory (Enterprise Edition), also known as AWS Managed Microsoft AD, that enables directory-aware workloads and AWS resources to use managed Active Directory in the AWS Cloud.

AWS Key Management Service (KMS)

  • is a managed service that makes it easy to create and control the encryption keys used to encrypt your data.
  • uses HSMs to protect the security of your keys.
  • integrates with most AWS services for seamless encryption of data at rest.

AWS Organizations

  • allows creation of AWS account groups, to more easily manage security and automation settings collectively
  • helps centrally manage multiple accounts to help scale.
  • helps control which AWS services are available to individual accounts using Service Control Policies (SCPs), automate new account creation, and simplify billing.

AWS Shield

  • is a managed Distributed Denial of Service (DDoS) protection service that safeguards web applications running on AWS.
  • provides always-on detection and automatic inline mitigations that minimize application downtime and latency.
  • provides two tiers: Shield Standard (free, automatic) and Shield Advanced (paid, enhanced protection with 24/7 DDoS Response Team access).

AWS WAF

  • is a web application firewall that helps protect web applications from common web exploits that could affect application availability, compromise security, or consume excessive resources.
  • gives complete control over which traffic to allow or block to web application by defining customizable web security rules.
  • integrates with CloudFront, Application Load Balancer, API Gateway, and AWS AppSync.

Amazon GuardDuty

  • is a threat detection service that continuously monitors AWS accounts, workloads, and data for malicious activity and anomalous behavior.
  • analyzes events from AWS CloudTrail, VPC Flow Logs, DNS logs, and other sources using machine learning and threat intelligence.
  • provides actionable security findings with severity levels for prioritized response.

Amazon Macie

  • is a data security service that discovers sensitive data using machine learning and pattern matching.
  • automatically discovers and protects sensitive data stored in Amazon S3, such as personally identifiable information (PII) and financial data.
  • provides visibility into data security risks and enables automated protection.

AWS Security Hub

  • provides a comprehensive view of your security posture across AWS accounts.
  • aggregates, organizes, and prioritizes security findings from multiple AWS services (GuardDuty, Inspector, Macie) and AWS Partner solutions.
  • automates security checks against best practices and industry standards.

Amazon Security Lake

  • automatically centralizes security data from AWS environments, SaaS providers, and on-premises sources into a purpose-built data lake.
  • normalizes data using the Open Cybersecurity Schema Framework (OCSF) for easier analysis.
  • stores data in your account using S3, giving you full control and ownership.

AWS Compute Services

Amazon Elastic Compute Cloud (EC2)

  • provides secure, resizable compute capacity
  • provides complete control of the computing resources (root access, ability to start, stop, terminate instances etc.)
  • reduces the time required to obtain and boot new instances to minutes
  • allows quick scaling of capacity, both up and down, as computing requirements change
  • provides developers and sysadmins tools to build failure-resilient applications and isolate themselves from common failure scenarios.
  • Benefits
    • Elastic Web-Scale Computing – enables scaling to increase or decrease capacity within minutes.
    • Flexible Cloud Hosting Services – flexibility to choose from multiple instance types (including AWS Graviton-based ARM instances for better price-performance), operating systems, and software packages.
    • Reliable – offers a highly reliable environment where replacement instances can be rapidly commissioned. EC2 SLA commitment is 99.99% availability for each Region.
    • Secure – works in conjunction with VPC to provide security and robust networking functionality. Allows control of IP address, exposure to Internet (using subnets), inbound and outbound access (using Security groups and NACLs).
    • Inexpensive – pay only for the capacity actually used
  • EC2 Purchasing Options
    • On-Demand Instances – pay for compute capacity by the hour or second with no long-term commitments.
    • Savings Plans – flexible pricing model offering up to 72% savings in exchange for a commitment to a consistent amount of usage (measured in $/hour) for a 1 or 3-year term. Available as Compute Savings Plans or EC2 Instance Savings Plans.
    • Reserved Instances – provides significant discount (up to 72%) compared to On-Demand pricing for a 1 or 3-year commitment to a specific instance type.
    • Spot Instances – allows use of spare EC2 computing capacity at up to 90% discount compared to On-Demand pricing. Instances can be interrupted by AWS with a 2-minute warning.
    • Dedicated Instances – run on hardware dedicated to a single customer for additional isolation.
    • Dedicated Hosts – physical servers with EC2 instance capacity fully dedicated to your use, allowing use of existing server-bound software licenses.

Amazon Elastic Container Service (ECS)

  • is a fully managed container orchestration service that supports Docker containers.
  • allows running applications on a managed cluster of EC2 instances or serverlessly with AWS Fargate.
  • eliminates the need to install, operate, and scale cluster management infrastructure.
  • can schedule the placement of containers across the cluster based on resource needs and availability requirements.
  • integrates with Elastic Load Balancing, VPC, IAM, CloudWatch, and other AWS services.

Amazon Elastic Kubernetes Service (EKS)

  • is a managed Kubernetes service that makes it easy to run Kubernetes on AWS without needing to install and operate your own Kubernetes control plane.
  • runs upstream Kubernetes, ensuring compatibility with existing Kubernetes applications and tools.
  • automatically manages the availability and scalability of the Kubernetes control plane nodes.
  • supports running pods on EC2 instances, AWS Fargate (serverless), or on-premises with EKS Anywhere.
  • EKS Auto Mode automatically provisions and manages compute, networking, and storage for Kubernetes clusters.

Amazon Elastic Container Registry (ECR)

  • is a fully managed Docker container registry that makes it easy to store, manage, and deploy Docker container images.
  • is integrated with Amazon ECS and EKS, simplifying development to production workflow.
  • eliminates the need to operate container repositories or worry about scaling the underlying infrastructure.
  • supports OCI images and artifacts, private and public repositories.

AWS Fargate

  • is a serverless compute engine for containers that works with both Amazon ECS and Amazon EKS.
  • removes the need to provision, configure, or scale clusters of virtual machines to run containers.
  • allocates the right amount of compute resources, eliminating the need to choose instance types or manage scaling.
  • each task or pod runs in its own isolated environment for workload isolation by design.

Amazon Lightsail

  • is designed to be the easiest way to launch and manage a virtual private server with AWS.
  • plans include everything needed to jumpstart a project – a virtual machine, SSD-based storage, data transfer, DNS management, and a static IP address – for a low, predictable price.

AWS Batch

  • enables developers, scientists, and engineers to easily and efficiently run hundreds of thousands of batch computing jobs on AWS.
  • dynamically provisions the optimal quantity and type of compute resources based on the volume and specific resource requirements of the batch jobs submitted.
  • plans, schedules, and executes the batch computing workloads across the full range of AWS compute services and features.

AWS Elastic Beanstalk

  • is an easy-to-use service for deploying and scaling web applications and services developed with Java, .NET, PHP, Node.js, Python, Ruby, Go, and Docker on familiar servers such as Apache, Nginx, Passenger, and IIS.
  • automatically handles the deployment, from capacity provisioning, load balancing, and auto scaling to application health monitoring.
  • provides full control over the AWS resources with access to the underlying resources at any time.

AWS Lambda

  • enables running code without provisioning or managing servers, with automatic scaling for high availability.
  • pay only for the compute time consumed – there is no charge when the code is not running.
  • can be triggered from other AWS services or called directly from any web or mobile app.
  • supports container images up to 10 GB, up to 10 GB of memory, and execution durations up to 15 minutes.
  • supports multiple runtimes including Node.js, Python, Java, .NET, Go, Ruby, and custom runtimes.

AWS App Runner

  • is a fully managed service for building, deploying, and running containerized web applications and APIs at scale.
  • automatically builds and deploys from source code or container images with no infrastructure management required.
  • handles load balancing, scaling, and TLS certificate management automatically.

Auto Scaling

  • helps maintain application availability
  • allows scaling EC2 capacity up or down automatically according to defined conditions or demand spikes to reduce cost
  • helps ensure desired number of EC2 instances are running always
  • AWS Auto Scaling provides unified scaling for multiple resources (EC2, ECS, DynamoDB, Aurora) through scaling plans.
  • supports target tracking, step scaling, and predictive scaling policies.

Storage

Amazon Simple Storage Service (S3)

  • is object storage with a simple web service interface to store and retrieve any amount of data from anywhere on the web.
  • S3 Features
    • Durable – designed for durability of 99.999999999% (11 nines) of objects. Data is redundantly stored across multiple facilities and multiple devices in each facility.
    • Available – designed for up to 99.99% availability (Standard) of objects over a given year.
    • Scalable – can store virtually unlimited data
    • Secure – supports data in transit over SSL and data at rest encryption. Bucket policies, ACLs, and IAM can manage object permissions. S3 Block Public Access provides account-level settings to prevent unintended public access.
    • Storage Classes – multiple classes for different use cases:
      • S3 Standard – frequently accessed data
      • S3 Intelligent-Tiering – automatically moves data between access tiers based on usage patterns
      • S3 Standard-IA – infrequently accessed data
      • S3 One Zone-IA – infrequently accessed, single-AZ
      • S3 Glacier Instant Retrieval – archive with millisecond retrieval
      • S3 Glacier Flexible Retrieval (formerly Glacier) – archive with minutes to hours retrieval
      • S3 Glacier Deep Archive – lowest-cost archive with 12-48 hour retrieval
    • Lifecycle Policies – automatically transition data between storage classes

Amazon Elastic Block Store (EBS)

  • provides persistent block storage volumes for use with EC2 instances
  • offers the consistent and low-latency performance needed to run workloads.
  • allows scaling up or down within minutes
  • EBS Features
    • High Performance Volumes – Choose between SSD-backed (gp3, io2 Block Express) or HDD-backed (st1, sc1) volumes for performance needs.
    • Availability – designed for 99.999% availability, automatically replicates within its Availability Zone.
    • Encryption – provides seamless support for data-at-rest and data-in-transit between EC2 instances and EBS volumes.
    • Snapshots – create point-in-time snapshots backed up to S3 for long-term durability. Supports EBS Snapshots Archive for low-cost long-term retention.

Amazon Elastic File System (EFS)

  • provides simple, scalable, elastic file storage for use with AWS compute services and on-premises resources.
  • storage capacity is elastic, growing and shrinking automatically as files are added and removed.
  • works in shared mode, where multiple compute instances can access an EFS file system at the same time (NFS protocol).
  • can be mounted on on-premises servers via AWS Direct Connect or VPN.
  • is designed for high availability and durability across multiple AZs.
  • offers Standard and One Zone storage classes, each with Infrequent Access tiers.

Amazon FSx

  • provides fully managed third-party file systems with native compatibility for various workloads.
  • FSx for Windows File Server – fully managed Windows native file system with SMB protocol support, Active Directory integration.
  • FSx for Lustre – high-performance file system for compute-intensive workloads (ML, HPC, media processing).
  • FSx for NetApp ONTAP – fully managed NetApp ONTAP file system with multi-protocol access.
  • FSx for OpenZFS – fully managed OpenZFS file system for Linux workloads.

AWS Storage Gateway

  • seamlessly enables hybrid storage between on-premises storage environments and the AWS Cloud
  • combines a multi-protocol storage appliance with highly efficient network connectivity to AWS cloud storage services.
  • provides three gateway types: S3 File Gateway, FSx File Gateway, Volume Gateway, and Tape Gateway.

AWS Backup

  • is a fully managed backup service that centralizes and automates the backup of data across AWS services.
  • supports EC2, EBS, RDS, DynamoDB, EFS, FSx, Storage Gateway, and more.
  • provides a central backup console, backup policies, and cross-Region/cross-account backup capabilities.

Databases

Amazon Aurora

  • is a MySQL and PostgreSQL compatible relational database engine
  • provides the speed and availability of high-end commercial databases with the simplicity and cost-effectiveness of open source databases.
  • Benefits
    • Highly Secure – provides network isolation using VPC, encryption at rest using KMS, and encryption of data in transit using SSL.
    • Highly Scalable – automatically grows storage as needed, up to 128 TB.
    • High Availability and Durability – designed for greater than 99.99% availability. Six copies of data replicated across three AZs. Instance failover typically requires less than 30 seconds.
    • Fully Managed – database management tasks like provisioning, patching, backup, recovery, and failover are automated.
    • Aurora Serverless v2 – automatically scales capacity up and down based on application demand, ideal for variable or unpredictable workloads.

Amazon Relational Database Service (RDS)

  • makes it easy to set up, operate, and scale a relational database
  • provides cost-efficient and resizable capacity while managing time-consuming database administration tasks
  • supports Amazon Aurora, PostgreSQL, MySQL, MariaDB, Oracle, and Microsoft SQL Server
  • Benefits
    • Fast and Easy to Administer – no need for infrastructure provisioning or database software installation and maintenance.
    • Highly Scalable – allows quick scaling of compute and storage resources. Read Replicas available to offload read traffic.
    • Available and Durable – Multi-AZ deployments synchronously replicate data to a standby instance in a different AZ. Automated backups, snapshots, and automatic host replacement.
    • Secure – network isolation using VPC, encryption at rest with KMS, encryption in transit with SSL.
    • Inexpensive – pay low rates with On-Demand or Reserved Instance pricing.
    • RDS Proxy – a fully managed database proxy that makes applications more scalable and resilient to database failures.

Amazon DynamoDB

  • is a fully managed, serverless, key-value and document NoSQL database designed for single-digit millisecond performance at any scale.
  • supports both document and key-value data models.
  • Benefits
    • Fast, Consistent Performance – designed to deliver consistent, fast performance at any scale using SSD storage and automatic partitioning.
    • Highly Scalable – manages all scaling to achieve specified throughput capacity. Supports on-demand and provisioned capacity modes.
    • Event-Driven Programming – DynamoDB Streams and integration with Lambda enable applications that automatically react to data changes.
    • Global Tables – provides fully managed multi-Region, multi-active replication for globally distributed applications.
    • DAX (DynamoDB Accelerator) – in-memory caching for DynamoDB delivering microsecond read latency.

Amazon ElastiCache

  • is a web service that makes it easy to deploy, operate, and scale an in-memory cache in the cloud.
  • helps improve the performance of web applications by allowing retrieval from fast, managed, in-memory caches instead of slower disk-based databases.
  • supports two open-source in-memory caching engines: Redis (now Valkey-compatible) and Memcached.

Amazon MemoryDB

  • is a durable, Redis/Valkey-compatible, in-memory database service for ultra-fast performance.
  • delivers microsecond reads and single-digit millisecond writes with Multi-AZ durability.
  • can be used as a primary database for applications requiring both high performance and data durability.

Amazon DocumentDB

  • is a fully managed document database service that supports MongoDB workloads.
  • designed for JSON data management at scale with automatic scaling storage.

Amazon Neptune

  • is a fully managed graph database service for building applications that work with highly connected datasets.
  • supports Property Graph and RDF models with Apache TinkerPop Gremlin and SPARQL query languages.

Amazon Keyspaces

  • is a scalable, highly available, and fully managed Apache Cassandra-compatible database service.
  • serverless – pay only for the resources you use and the table automatically scales up and down.

Migration

AWS Application Discovery Service

  • helps plan application migration projects by automatically identifying applications running in on-premises data centers, their associated dependencies, and performance profiles.
  • automatically collects configuration and usage data from servers, storage, and networking equipment.
  • information is retained in encrypted format and can be exported for use with visualization tools or cloud migration solutions.

AWS Database Migration Service (DMS)

  • helps migrate databases to AWS easily and securely
  • source database remains fully operational during the migration, minimizing downtime.
  • supports homogeneous migrations (e.g., Oracle to Oracle) and heterogeneous migrations (e.g., Oracle to Aurora, SQL Server to MySQL).
  • allows streaming data to Redshift, S3, and other targets from supported sources.
  • can also be used for continuous data replication with high availability.
  • AWS Schema Conversion Tool (SCT) helps convert database schemas between different database engines.

AWS Application Migration Service (AWS MGN / AWS Transform MGN)

  • is the recommended service for lift-and-shift (rehost) migrations to AWS, replacing the deprecated AWS Server Migration Service.
  • automates the conversion of source servers (physical, virtual, or cloud) into native Amazon EC2 instances.
  • provides continuous block-level replication, short cutover windows, and automated testing.
  • Note: Previously called AWS Application Migration Service (MGN), now rebranded as AWS Transform MGN (June 2026).

AWS Snow Family

⚠️ Note: The AWS Snow Family is being wound down. As of November 2025, Snowball Edge devices are only available to existing customers. New customers should use AWS DataSync, AWS Data Transfer Terminal, or AWS Partner solutions.

  • AWS Snowball Edge (existing customers only) – a data transfer and edge computing device with on-board storage and compute capabilities. Can move large amounts of data and support local workloads.
  • AWS Snowmobile – Retired (March 2024). No longer available.
  • Migration Alternatives:
    • AWS DataSync – online data transfer service for automated transfer between on-premises and AWS storage.
    • AWS Data Transfer Terminal – secure physical location for transferring data to AWS.
    • AWS Transfer Family – fully managed SFTP, FTPS, FTP, and AS2 service for file transfers to S3 or EFS.

Networking and Content Delivery

Amazon Virtual Private Cloud (VPC)

  • helps provision a logically isolated section of the AWS Cloud where AWS resources can be launched in a virtual network that you define.
  • provides complete control over the virtual networking environment, including selection of IP address range, creation of subnets (public and private), and configuration of route tables and network gateways.
  • allows use of both IPv4 and IPv6 for secure and easy access to resources.
  • allows multiple layers of security, including security groups and network access control lists (NACLs).
  • allows creation of VPN connections between corporate data center and VPC.
  • VPC Peering enables private connectivity between VPCs. Transit Gateway provides a hub for connecting multiple VPCs and on-premises networks.

Amazon CloudFront

  • is a global content delivery network (CDN) service that accelerates delivery of websites, APIs, video content, or other web assets.
  • can deliver entire website, including dynamic, static, streaming, and interactive content using a global network of edge locations.
  • requests for content are automatically routed to the nearest edge location for best possible performance.
  • is optimized to work with S3, EC2, ELB, Route 53, and API Gateway as well as non-AWS origin servers.
  • supports edge functions via CloudFront Functions and Lambda@Edge for customizing content at the edge.

Amazon Route 53

  • is a highly available and scalable Domain Name System (DNS) web service.
  • connects user requests to infrastructure running in AWS or outside of AWS.
  • helps configure DNS health checks to route traffic to healthy endpoints.
  • allows traffic management globally through latency-based routing, Geo DNS, geoproximity, weighted round robin, multivalue answer, and IP-based routing – all combinable with DNS Failover.
  • is fully compliant with IPv6 and offers Domain Name Registration service.

AWS Direct Connect

  • makes it easy to establish a dedicated network connection from on-premises to AWS.
  • helps establish private connectivity between AWS and data center, office, or co-location environment.
  • helps increase bandwidth throughput, reduce network costs, and provide a more consistent network experience than Internet-based connections.

Elastic Load Balancing (ELB)

  • automatically distributes incoming application traffic across multiple targets (EC2 instances, containers, IP addresses, Lambda functions).
  • enables greater levels of fault tolerance by seamlessly providing the required amount of load balancing capacity.
  • offers four types of load balancers:
    • Application Load Balancer (ALB) – operates at Layer 7 (HTTP/HTTPS). Routes traffic based on content of the request. Ideal for microservices, container-based architectures, and advanced routing needs.
    • Network Load Balancer (NLB) – operates at Layer 4 (TCP/UDP/TLS). Handles millions of requests per second with ultra-low latency. Ideal for TCP/UDP traffic and extreme performance requirements.
    • Gateway Load Balancer (GWLB) – operates at Layer 3 (IP). Makes it easy to deploy, scale, and manage third-party virtual appliances (firewalls, IDS/IPS). Combines transparent network gateway with load balancing.
    • Classic Load Balancer (CLB) – previous generation, operates at both Layer 4 and Layer 7. Recommended to migrate to ALB or NLB.

AWS Global Accelerator

  • is a networking service that improves the availability and performance of applications by using the AWS global network.
  • provides two static anycast IP addresses that serve as a fixed entry point to applications hosted in one or more AWS Regions.
  • continuously monitors endpoints and instantly routes traffic to the closest healthy endpoint.

AWS PrivateLink

  • provides private connectivity between VPCs, AWS services, and on-premises applications without exposing traffic to the public internet.
  • simplifies security of data shared between cloud-based applications and on-premises services.

Management and Governance

Amazon CloudWatch

  • is a monitoring and observability service for AWS Cloud resources and the applications running on AWS.
  • can collect and track metrics, collect and monitor log files, set alarms, and automatically react to changes in AWS resources.
  • provides CloudWatch Logs, Metrics, Alarms, Dashboards, and Events (now EventBridge) for comprehensive monitoring.
  • supports custom metrics, anomaly detection, and cross-account observability.

AWS CloudFormation

  • allows developers and systems administrators to implement “Infrastructure as Code”
  • provides an easy way to create and manage a collection of related AWS resources, provisioning and updating them in an orderly and predictable fashion.
  • handles the order for provisioning AWS services and the subtleties of making those dependencies work.
  • allows applying version control to AWS infrastructure the same way it’s done with software.
  • AWS CDK (Cloud Development Kit) allows defining infrastructure using familiar programming languages (TypeScript, Python, Java, etc.) that synthesize to CloudFormation templates.

AWS CloudTrail

  • records AWS API calls for the account and delivers log files.
  • includes API calls made via the Console, CLI, SDKs, and higher-level AWS services.
  • recorded information includes the identity of the API caller, time, source IP address, request parameters, and response elements.
  • enables security analysis, resource change tracking, compliance auditing, and operational troubleshooting.
  • supports CloudTrail Lake for SQL-based querying and long-term retention of events.

AWS Config

  • provides an AWS resource inventory, configuration history, and configuration change notifications to enable security and governance.
  • provides Config Rules feature that enables creation of rules to automatically check the configuration of AWS resources.
  • helps discover existing and deleted AWS resources, determine overall compliance against rules, and dive into configuration details at any point in time.
  • supports Conformance Packs for packaging multiple Config Rules and remediation actions together.

AWS Systems Manager

  • provides a unified user interface to view operational data from multiple AWS services and automate operational tasks across AWS resources.
  • includes capabilities for patch management, configuration management, session management, parameter store, and run command.
  • helps maintain security and compliance by scanning managed instances for patch compliance and configuration inconsistencies.

AWS Service Catalog

  • allows organizations to create and manage catalogs of IT services approved for use on AWS.
  • helps centrally manage commonly deployed IT services and helps achieve consistent governance and compliance requirements.

AWS Trusted Advisor

  • is an online resource that inspects your AWS environment and provides recommendations across five categories: cost optimization, performance, security, fault tolerance, and service limits.
  • provides real-time guidance to help provision resources following AWS best practices.

AWS Health Dashboard

  • provides alerts and remediation guidance when AWS is experiencing events that might affect you (formerly Personal Health Dashboard).
  • displays relevant information to help manage events in progress and provides proactive notification for scheduled activities.
  • provides a personalized view into the performance and availability of AWS services underlying your resources.

AWS Control Tower

  • provides the easiest way to set up and govern a secure, multi-account AWS environment (landing zone).
  • establishes a well-architected multi-account baseline with guardrails (preventive and detective) for governance.
  • automates account provisioning and applies best practices for identity management, federated access, and logging.

Developer Tools

AWS CodeCommit

  • is a fully managed source control service that hosts secure and highly scalable private Git repositories.
  • ⚠️ Note: CodeCommit is no longer available to new customers (July 2024). Existing customers can continue using it. Consider GitHub, GitLab, or Bitbucket as alternatives.

AWS CodeBuild

  • is a fully managed build service that compiles source code, runs tests, and produces software packages that are ready to deploy.
  • scales continuously and processes multiple builds concurrently.

AWS CodeDeploy

  • is a service that automates code deployments to any instance, including EC2 instances, Lambda functions, ECS services, and on-premises servers.
  • helps rapidly release new features, avoid downtime during deployment, and handles the complexity of updating applications.

AWS CodePipeline

  • is a continuous integration and continuous delivery (CI/CD) service for fast and reliable application and infrastructure updates.
  • builds, tests, and deploys code every time there is a code change, based on defined release process models.

AWS X-Ray

  • helps developers analyze and debug distributed applications in production, such as those built using microservices architectures.
  • provides an end-to-end view of requests as they travel through the application, and shows a map of its underlying components.
  • helps identify and troubleshoot the root cause of performance issues and errors.

Amazon Q Developer

  • is a generative AI-powered assistant for software development (formerly Amazon CodeWhisperer).
  • provides AI-powered code suggestions, security scanning, code transformation, and natural language chat for development tasks.
  • supports multiple IDEs and programming languages.

Messaging and Application Integration

Amazon SQS

  • is a fast, reliable, scalable, fully managed message queuing service.
  • makes it simple and cost-effective to decouple the components of a cloud application.
  • includes Standard queues with high throughput and at-least-once processing, and FIFO queues with exactly-once processing and ordered delivery.

Amazon SNS

  • is a fast, flexible, fully managed pub/sub messaging and mobile notification service.
  • can send notifications to Apple, Google, Windows, and other mobile platforms, email, SMS, HTTP endpoints, SQS queues, and Lambda functions.
  • supports message filtering, FIFO topics, and message archiving.

Amazon SES

  • is a cost-effective, scalable email service for sending transactional email, marketing messages, or any other type of high-quality content.
  • can also receive messages and deliver them to S3, trigger Lambda functions, or publish to SNS.

Amazon EventBridge

  • is a serverless event bus that makes it easy to connect applications using data from your own apps, SaaS apps, and AWS services.
  • delivers a stream of real-time data from event sources and routes that data to targets like Lambda, Step Functions, SQS, and more.
  • replaces CloudWatch Events with additional capabilities including schema registry and third-party integrations.

AWS Step Functions

  • makes it easy to coordinate the components of distributed applications and microservices using visual workflows.
  • automatically triggers and tracks each step, and retries when there are errors.
  • supports Standard Workflows (long-running) and Express Workflows (high-volume, short-duration).

Amazon API Gateway

  • is a fully managed service for creating, publishing, maintaining, monitoring, and securing APIs at any scale.
  • handles traffic management, authorization, access control, monitoring, and API version management.
  • supports REST APIs, HTTP APIs, and WebSocket APIs.

Analytics

Amazon Athena

  • is an interactive query service that helps analyze data in S3 using standard SQL.
  • is serverless – no infrastructure to manage, pay only for queries run.
  • supports querying data in multiple formats including CSV, JSON, ORC, Avro, and Parquet.
  • integrates with AWS Glue Data Catalog for schema management.

Amazon EMR

  • provides a managed big data platform that makes it easy, fast, and cost-effective to process vast amounts of data.
  • supports Apache Spark, Hive, HBase, Presto, Flink, and other popular frameworks.
  • can run on EC2, EKS, or serverlessly with EMR Serverless.
  • handles big data use cases including log analysis, ETL, machine learning, and scientific simulation.

Amazon OpenSearch Service

  • makes it easy to deploy, operate, and scale OpenSearch (and legacy Elasticsearch) for log analytics, full-text search, application monitoring, and more.
  • Note: Renamed from Amazon Elasticsearch Service in September 2021.
  • is a fully managed service delivering real-time search and analytics capabilities along with availability, scalability, and security for production workloads.
  • supports OpenSearch Dashboards (successor to Kibana) for data visualization.

Amazon Kinesis

  • is a platform for streaming data on AWS, offering services to collect, process, and analyze real-time streaming data.
  • offers:
    • Amazon Kinesis Data Streams – enables building custom applications that process or analyze streaming data for specialized needs.
    • Amazon Data Firehose (formerly Kinesis Data Firehose) – easiest way to capture, transform, and load streaming data into S3, Redshift, OpenSearch, and third-party services like Splunk and Snowflake.
    • Amazon Managed Service for Apache Flink (formerly Kinesis Data Analytics) – process and analyze streaming data in real time using Apache Flink.
    • Amazon Kinesis Video Streams – capture, process, and store video streams for analytics and machine learning.

Amazon Redshift

  • provides a fast, fully managed, petabyte-scale cloud data warehouse.
  • uses massively parallel processing (MPP) architecture, parallelizing and distributing SQL operations across nodes.
  • supports Redshift Serverless for running analytics without managing infrastructure.
  • provides Redshift Spectrum to query data directly in S3 without loading it.

Amazon QuickSight

  • is a fast, cloud-powered business intelligence (BI) service for building visualizations, performing ad-hoc analysis, and getting business insights from data.
  • supports ML-powered insights with Amazon Q in QuickSight for natural language querying.

AWS Glue

  • is a serverless data integration service that makes it easy to discover, prepare, move, and integrate data from multiple sources.
  • provides the Glue Data Catalog as a central metadata repository.
  • simplifies and automates data discovery, ETL job authoring, and job scheduling.
  • scales automatically and provisions resources as needed.

AWS Lake Formation

  • makes it easy to set up a secure data lake in days instead of months.
  • provides centralized governance and security for data lake access using fine-grained permissions.

Machine Learning and Artificial Intelligence

Amazon Bedrock

  • is a fully managed service offering access to leading foundation models (FMs) from AI companies (Anthropic, Meta, Mistral, Amazon, and others) through a single API.
  • provides capabilities to build generative AI applications with security, privacy, and responsible AI features.
  • supports use cases like text generation, summarization, image generation, chatbots, and AI agents.
  • offers Bedrock Agents for building autonomous AI agents and Bedrock Knowledge Bases for RAG (Retrieval Augmented Generation).

Amazon SageMaker

  • is a fully managed machine learning service to build, train, and deploy ML models at scale.
  • provides SageMaker Studio as a unified IDE for ML development.
  • supports the entire ML workflow: data preparation, model building, training, tuning, and deployment.
  • includes built-in algorithms, pre-built ML frameworks, and AutoML capabilities.

Amazon Rekognition

  • makes it easy to add image and video analysis to applications using deep learning technology.
  • can identify objects, people, text, scenes, and activities, and detect inappropriate content.

Amazon Comprehend

  • is a natural language processing (NLP) service that uses machine learning to find insights and relationships in text.
  • can identify the language, extract key phrases, sentiment, entities, and topics.

Amazon Lex

  • is a service for building conversational interfaces using voice and text (same technology that powers Alexa).
  • provides automatic speech recognition (ASR) and natural language understanding (NLU).

Amazon Polly

  • is a text-to-speech service that turns text into lifelike speech using deep learning.
  • supports multiple languages and provides a variety of natural-sounding voices.

Amazon Transcribe

  • is an automatic speech recognition (ASR) service that converts speech to text.
  • supports real-time transcription and batch transcription of audio files.

Amazon Translate

  • is a neural machine translation service for fast, high-quality language translation.
  • supports translation between supported languages for applications and content.

Cloud Financial Management

AWS Cost Explorer

  • provides an easy-to-use interface to visualize, understand, and manage AWS costs and usage over time.
  • offers forecasting, savings recommendations, and detailed filtering/grouping of cost data.

AWS Budgets

  • allows setting custom budgets that alert when costs or usage exceed (or are forecasted to exceed) the budgeted amount.
  • supports cost, usage, reservation, and savings plans budgets.

AWS Pricing Calculator

  • helps estimate the cost of using AWS services before deployment.
  • allows creating cost estimates for various architectures and configurations.

Deprecated Services (Historical Reference)

The following services mentioned in the original AWS Overview Whitepaper have been deprecated or discontinued. They are listed here for reference and certification context.

  • Amazon Cloud Directory – No longer open to new customers (November 2025). Alternatives: DynamoDB, Neptune.
  • AWS OpsWorks – Reached End of Life on May 26, 2024. Disabled for all customers. Alternatives: AWS Systems Manager, CloudFormation, CodeDeploy.
  • Amazon Elastic Transcoder – Discontinued November 13, 2025. Replaced by AWS Elemental MediaConvert.
  • AWS Server Migration Service (SMS) – Deprecated. Replaced by AWS Application Migration Service (MGN / Transform MGN).
  • AWS Data Pipeline – No longer available to new customers (July 2024). Alternatives: AWS Glue, Step Functions, Amazon MWAA (Managed Workflows for Apache Airflow).
  • Amazon SWF (Simple Workflow Service) – Still operational but superseded by AWS Step Functions for new workloads.
  • AWS Snowmobile – Retired March 2024. No longer available.
  • Amazon CodeCatalyst – No longer open to new customers (November 2025).

AWS Certification Exam Practice Questions

  • Questions are collected from Internet and the answers are marked as per my knowledge and understanding (which might differ with yours).
  • AWS services are updated everyday and both the answers and questions might be outdated soon, so research accordingly.
  • AWS exam questions are not updated to keep up the pace with AWS updates, so even if the underlying feature has changed the question might not be updated
  • Open to further feedback, discussion and correction.
  1. Which AWS services belong to the Compute services? Choose 2 answers
    1. Lambda
    2. EC2
    3. S3
    4. EMR
    5. CloudFront
  2. Which AWS service provides low cost storage option for archival and long-term backup?
    1. S3 Glacier
    2. S3 Standard
    3. EBS
    4. CloudFront
  3. Which AWS services belong to the Storage services? Choose 2 answers
    1. EFS
    2. IAM
    3. EMR
    4. S3
    5. CloudFront
  4. A Company allows users to upload videos on its platform. They want to convert the videos to multiple formats supported on multiple devices and platforms. Which AWS service can they leverage for the requirement?
    1. AWS SWF
    2. AWS Video Converter
    3. AWS Elemental MediaConvert
    4. AWS Data Pipeline
  5. Which analytic service helps analyze data in S3 using standard SQL?
    1. Athena
    2. EMR
    3. OpenSearch
    4. Kinesis
  6. What features does AWS’s Route 53 service provide? Choose the 2 correct answers:
    1. Content Caching
    2. Domain Name System (DNS) service
    3. Database Management
    4. Domain Registration
  7. You are trying to organize and import (to AWS) gigabytes of data that are currently structured in JSON-like, name-value documents. What AWS service would best fit your needs?
    1. Lambda
    2. DynamoDB
    3. RDS
    4. Aurora
  8. What AWS database is primarily used to analyze data using standard SQL formatting with compatibility for your existing business intelligence tools? Choose the correct answer:
    1. Redshift
    2. RDS
    3. DynamoDB
    4. ElastiCache
  9. A company wants their application to use pre-configured machine image with software installed and configured. Which AWS feature can help for the same?
    1. Amazon Machine Image (AMI)
    2. AWS CloudFormation
    3. AWS Lambda
    4. AWS Lightsail
  10. What AWS service can be used to track API event calls for security analysis and resource change tracking?
    1. AWS CloudWatch
    2. AWS CloudFormation
    3. AWS CloudTrail
    4. AWS Systems Manager
  11. Which AWS service can help offload the read traffic from your database in order to reduce latency caused by read-heavy workload?
    1. ElastiCache
    2. DynamoDB
    3. S3
    4. EFS
  12. What service allows system administrators to run “Infrastructure as Code”?
    1. CloudFormation
    2. CloudWatch
    3. CloudTrail
    4. CodeDeploy
  13. Which AWS service is a fully managed container orchestration service?
    1. EC2
    2. Amazon ECS
    3. AWS Lambda
    4. Amazon S3
  14. A company wants to run containers without managing servers or clusters. Which AWS service should they use?
    1. Amazon EC2
    2. Amazon EKS on EC2
    3. AWS Fargate
    4. AWS Batch
  15. Which AWS service provides a fully managed generative AI service with access to foundation models?
    1. Amazon SageMaker
    2. Amazon Bedrock
    3. Amazon Comprehend
    4. Amazon Rekognition
  16. Which Elastic Load Balancer type operates at Layer 4 and is best suited for ultra-low latency TCP/UDP traffic?
    1. Application Load Balancer
    2. Network Load Balancer
    3. Gateway Load Balancer
    4. Classic Load Balancer
  17. Which AWS service provides centralized threat detection by continuously monitoring AWS accounts and workloads for malicious activity?
    1. AWS WAF
    2. Amazon Inspector
    3. Amazon GuardDuty
    4. AWS Shield
  18. A company wants to save costs on EC2 by committing to a consistent usage amount ($/hour) for 1-3 years with flexibility across instance families, regions, and services. What should they use?
    1. Reserved Instances
    2. Spot Instances
    3. Compute Savings Plans
    4. Dedicated Hosts

References

AWS Support Plans

AWS Support Plans

⚠️ Major Update: AWS Support Plans Transformation (Dec 2025)

At AWS re:Invent 2025, AWS announced a fundamental restructuring of Support Plans. The legacy Developer, Business, and Enterprise On-Ramp plans will be discontinued on January 1, 2027.

New plan structure (effective 2026):

  • Basic (Free) — included for all AWS customers
  • Business Support+ — replaces Developer and Business (starts at $29/month)
  • Enterprise Support — enhanced with AI capabilities (starts at $5,000/month)
  • Unified Operations — new highest tier (starts at $50,000/month)

Legacy plan customers can transition anytime before Jan 1, 2027. Enterprise On-Ramp customers are being automatically upgraded to Enterprise Support throughout 2026.

NOTE – This post is relevant for AWS Cloud Practitioner Certification and AWS Solutions Architect Associate Certification

Current AWS Support Plans (2026+)

AWS now offers three paid support plans plus the free Basic tier. Each plan combines AI-powered capabilities with AWS expert guidance, representing a shift from reactive problem-solving to proactive issue prevention.

Basic (Free)

  • Included for all AWS customers at no cost
  • 24×7 access to customer service, documentation, whitepapers, and re:Post community forums
  • Access to AWS Health Dashboard (formerly Personal Health Dashboard) for service health notifications
  • Access to limited AWS Trusted Advisor checks (core security checks)
  • Access to AWS Support Automation Workflows for self-service troubleshooting

Business Support+

Replaces the legacy Developer and Business Support plans. Starts at $29/month per account.

  • 24×7 access to AWS Cloud Support Engineers via email, chat & phone
  • AI-powered contextual troubleshooting that understands your specific AWS environment
  • Allows Unlimited contacts/Unlimited cases (IAM supported)
  • Access to full set of AWS Trusted Advisor checks
  • Access to AWS Health Dashboard & Health API
  • Access to AWS DevOps Agent for automated incident investigation and prevention
  • Access to AWS Support App in Slack
  • Proactive health checks with actionable recommendations across security, performance, cost, and reliability
  • Case Severity/Response times SLA:
    • General guidance < 24 hours
    • System impaired < 12 hours
    • Production system impaired < 4 hours
    • Business-critical system down < 30 minutes
  • Pricing: Greater of $29/month per account OR tiered % of monthly AWS charges (9% up to $10K, 7% $10K-$80K, 5% $80K-$250K, 3% over $250K)

Enterprise Support

Enhanced with AI capabilities. Starts at $5,000/month (reduced from previous $15,000 minimum).

  • 24×7 access to Sr. Cloud Support Engineers via email, chat & phone
  • Designated Technical Account Manager (TAM) for strategic guidance and proactive engagement
  • AI-powered intelligent troubleshooting with personalized context delivery to support engineers
  • AWS Security Incident Response — automated security monitoring, triage, and 24/7 access to security engineers (included at no additional cost)
  • Access to AWS DevOps Agent with 75% credits of monthly support charge
  • TAM-led Well-Architected Reviews and architectural assessments
  • Access to AWS Trusted Advisor Priority with 465+ best practice checks across 56+ services
  • Account assistance by Support Concierge
  • Access to online self-paced labs and TAM-led workshops
  • AWS Countdown Premium available as add-on ($10K/project/month) for critical launches, migrations, and peak events
  • Case Severity/Response times SLA:
    • General guidance < 24 hours
    • System impaired < 12 hours
    • Production system impaired < 4 hours
    • Production system down < 1 hour
    • Business-critical system down < 15 minutes
  • Pricing: Greater of $5,000/month OR tiered % of monthly AWS charges (10% up to $150K, 7% $150K-$500K, 5% $500K-$1M, 3% over $1M)

Unified Operations

New highest-tier plan for mission-critical enterprise operations. Starts at $50,000/month.

  • Designated core team: Technical Account Manager (TAM), Domain Specialist Engineers (DSE), and Senior Billing & Account Specialist
  • On-demand experts for migrations, incident management, and security
  • 24/7 proactive security and performance monitoring with early incident detection
  • AWS Security Incident Response with AI-powered investigation included
  • AWS DevOps Agent with 100% credits of monthly support charge
  • AWS Countdown Premium included at no additional cost
  • AWS Incident Detection and Response included at no additional cost
  • Expert-led resilience reviews, GameDay exercises, and chaos engineering
  • Critical Workload Reviews and comprehensive architecture assessments
  • Support via preferred collaboration channels (follow-the-sun model)
  • Case Severity/Response times SLA:
    • General guidance < 24 hours
    • System impaired < 12 hours
    • Production system impaired < 4 hours
    • Production system down < 1 hour
    • Business-critical system down < 5 minutes
  • Pricing: Greater of $50,000/month OR tiered % of monthly AWS charges (10% up to $1M, 6% $1M-$5M, 5% over $5M). Minimum 90-day commitment.

Legacy Plans (Discontinued January 1, 2027)

⚠️ The following plans are being discontinued on January 1, 2027. Existing customers can continue using them until that date or transition to new plans anytime.

Developer (Legacy)

Migrates to → Business Support+

  • Business hours access to Cloud Support Associates via email
  • One primary contact can open Unlimited cases
  • Case Severity/Response times SLA (in business hours):
    • General guidance < 24 business hours
    • System impaired < 12 business hours
  • General Guidance on Architecture support

Business (Legacy)

Migrates to → Business Support+

  • 24×7 access to Cloud Support Engineers via email, chat & phone
  • Unlimited contacts/Unlimited cases (IAM supported)
  • Full set of Trusted Advisor checks
  • Case Severity/Response times:
    • General guidance < 24 hours
    • System impaired < 12 hours
    • Production system impaired < 4 hours
    • Production system down < 1 hour

Enterprise On-Ramp (Legacy)

Automatically upgrading to → Enterprise Support throughout 2026

  • Access to a pool of Technical Account Managers (not designated)
  • Consultative architectural guidance
  • Case Severity/Response times:
    • Business-critical system down < 30 minutes

Key Features Comparison

Feature Basic Business Support+ Enterprise Unified Operations
Critical response time — 30 min 15 min 5 min
24×7 expert access — ✓ ✓ ✓
Technical Account Manager — — Designated Designated + DSE team
AI-powered troubleshooting — ✓ ✓ ✓
AWS Security Incident Response — — Included Included
AWS DevOps Agent — 30% credits 75% credits 100% credits
Trusted Advisor Core checks Full checks Priority (465+ checks) Priority (465+ checks)
Well-Architected Reviews — — TAM-led Expert-led (comprehensive)
Minimum monthly cost Free $29/account $5,000 $50,000

AWS Support Plan Key Services

AWS Health Dashboard

  • Previously known as Personal Health Dashboard (PHD) and Service Health Dashboard (SHD)
  • Unified dashboard combining service health and account-specific health events
  • Provides personalized notifications about AWS service events affecting your resources
  • Available to all AWS customers (Basic and above)
  • Programmatic access via AWS Health API available with Business Support+ and above

AWS Trusted Advisor

  • Provides real-time recommendations across cost optimization, performance, security, fault tolerance, service limits, and operational excellence
  • Basic/Free: Core security checks only
  • Business Support+: Full set of Trusted Advisor checks
  • Enterprise/Unified Operations: Trusted Advisor Priority with 465+ checks across 56+ services, curated by TAM

AWS DevOps Agent

  • AI-powered operations teammate that autonomously investigates incidents 24/7
  • Provides proactive recommendations to prevent future outages
  • One-click case creation with full investigation context for AWS Support Engineers
  • Available to Business Support+ (30% credits), Enterprise (75% credits), Unified Operations (100% credits)

AWS Security Incident Response

  • Automated security finding monitoring and triage across GuardDuty and Security Hub
  • AI-powered investigation and containment capabilities
  • 24/7 access to AWS Security Incident Response engineers
  • Included with Enterprise and Unified Operations at no additional cost

AWS Certification Exam Practice Questions

  • Questions are collected from Internet and the answers are marked as per my knowledge and understanding (which might differ with yours).
  • AWS services are updated everyday and both the answers and questions might be outdated soon, so research accordingly.
  • AWS exam questions are not updated to keep up the pace with AWS updates, so even if the underlying feature has changed the question might not be updated
  • Open to further feedback, discussion and correction.
  1. Which AWS support plan has a designated technical account manager assigned for proactive guidance?
    1. AWS Basic support plan
    2. AWS Business Support+ plan
    3. AWS Enterprise Support plan
    4. AWS Unified Operations plan

    Note: Both Enterprise and Unified Operations have a designated TAM, but Enterprise is the first tier to include one.

  2. Which feature is available for all the AWS support plans?
    1. Technical Account Manager
    2. AWS DevOps Agent
    3. 24×7 access to customer service and AWS Health Dashboard
    4. AI-powered troubleshooting
  3. A company needs 24/7 access to AWS Support Engineers and AI-powered contextual troubleshooting at the lowest cost. Which AWS Support plan should they choose?
    1. Basic
    2. Business Support+
    3. Enterprise Support
    4. Unified Operations
  4. Which AWS Support plan provides a 5-minute response time for business-critical system failures?
    1. Business Support+
    2. Enterprise Support
    3. Unified Operations
    4. Basic
  5. What happens to customers on the legacy AWS Developer Support plan after January 1, 2027?
    1. They are automatically upgraded to Enterprise Support
    2. They lose all support access
    3. The plan is discontinued; they should upgrade to Business Support+ before that date
    4. They are moved to Basic support
  6. Which AWS Support plan includes AWS Security Incident Response at no additional cost?
    1. Basic
    2. Business Support+
    3. Enterprise Support
    4. Developer (Legacy)
  7. A startup needs AWS Support with expert access and the lowest minimum monthly cost. Which plan should they choose?
    1. Enterprise Support ($5,000/month minimum)
    2. Business Support+ ($29/month per account minimum)
    3. Unified Operations ($50,000/month minimum)
    4. Basic (free, no expert access)
  8. Which team members are included as part of the designated core team in the AWS Unified Operations plan? (Select TWO)
    1. Technical Account Manager (TAM)
    2. Solutions Architect
    3. Domain Specialist Engineers (DSE)
    4. AWS Account Executive

References